SBOM in IoT: Management and Implementation Strategies - Part 2
- 01 SBOM: A Prerequisite for Software Security – Part 1Read →
- 02 SBOM in IoT: Management and Implementation Strategies - Part 2Now reading
Contents
1️⃣ Why SBOM Management Matters for IoT Products
IoT products are unique in that they combine hardware, firmware, open-source, and third-party software into one interconnected system.
While this creates innovation, it also introduces complexity—meaning a single vulnerability can impact the security and reliability of an entire product line.
Key Characteristics of IoT Products
Complex Architecture: Built from hardware, firmware, open-source components, and third-party libraries.
Component Diversity: Heavy reliance on open-source due to the wide range of platforms and chipsets.
Long Lifecycles: Devices are deployed for years in the field, often with limited updates.
High Propagation Risk: One vulnerability can cascade across the entire product family.
Because IoT devices are designed for long-term use, vulnerability responses are often slow.
That’s why it is critical to maintain a traceable Software Bill of Materials (SBOM) that captures every component’s origin, version, and supplier.
2️⃣ Global SBOM Requirements in IoT Security Regulations
Across industries, major global regulations already require or strongly recommend SBOM adoption.
Preparing early is essential for compliance.

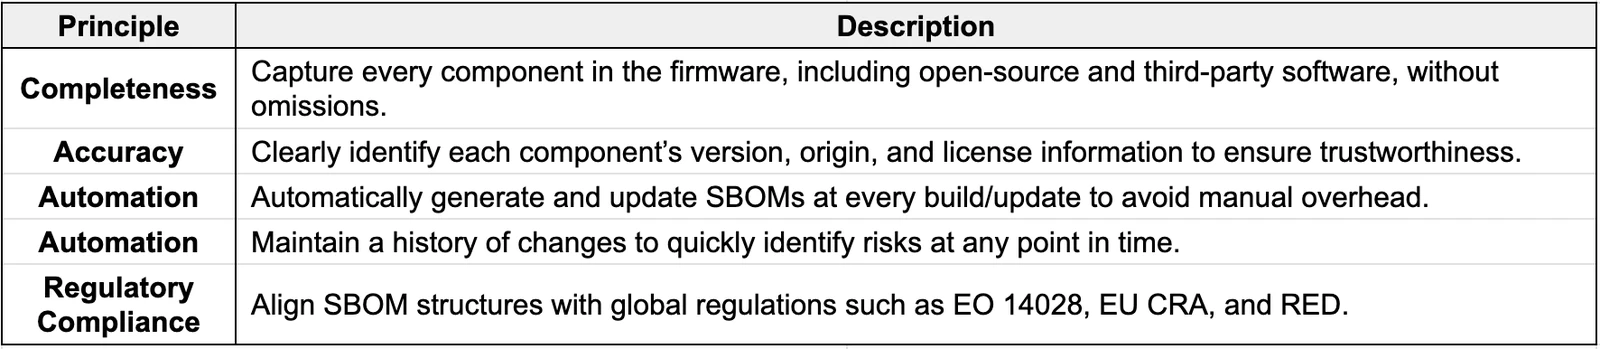
3️⃣ Five Core Principles of SBOM Management
To strengthen IoT firmware security, ZIEN recommends five key principles for effective SBOM management:
4️⃣ Automating SBOM Generation with Z-IoT
ZIEN’s Z-IoT solution automates SBOM creation and regulatory compliance, reducing the burden on security teams.
More than just listing packages, Z-IoT uncovers hidden components and provides detailed insights.
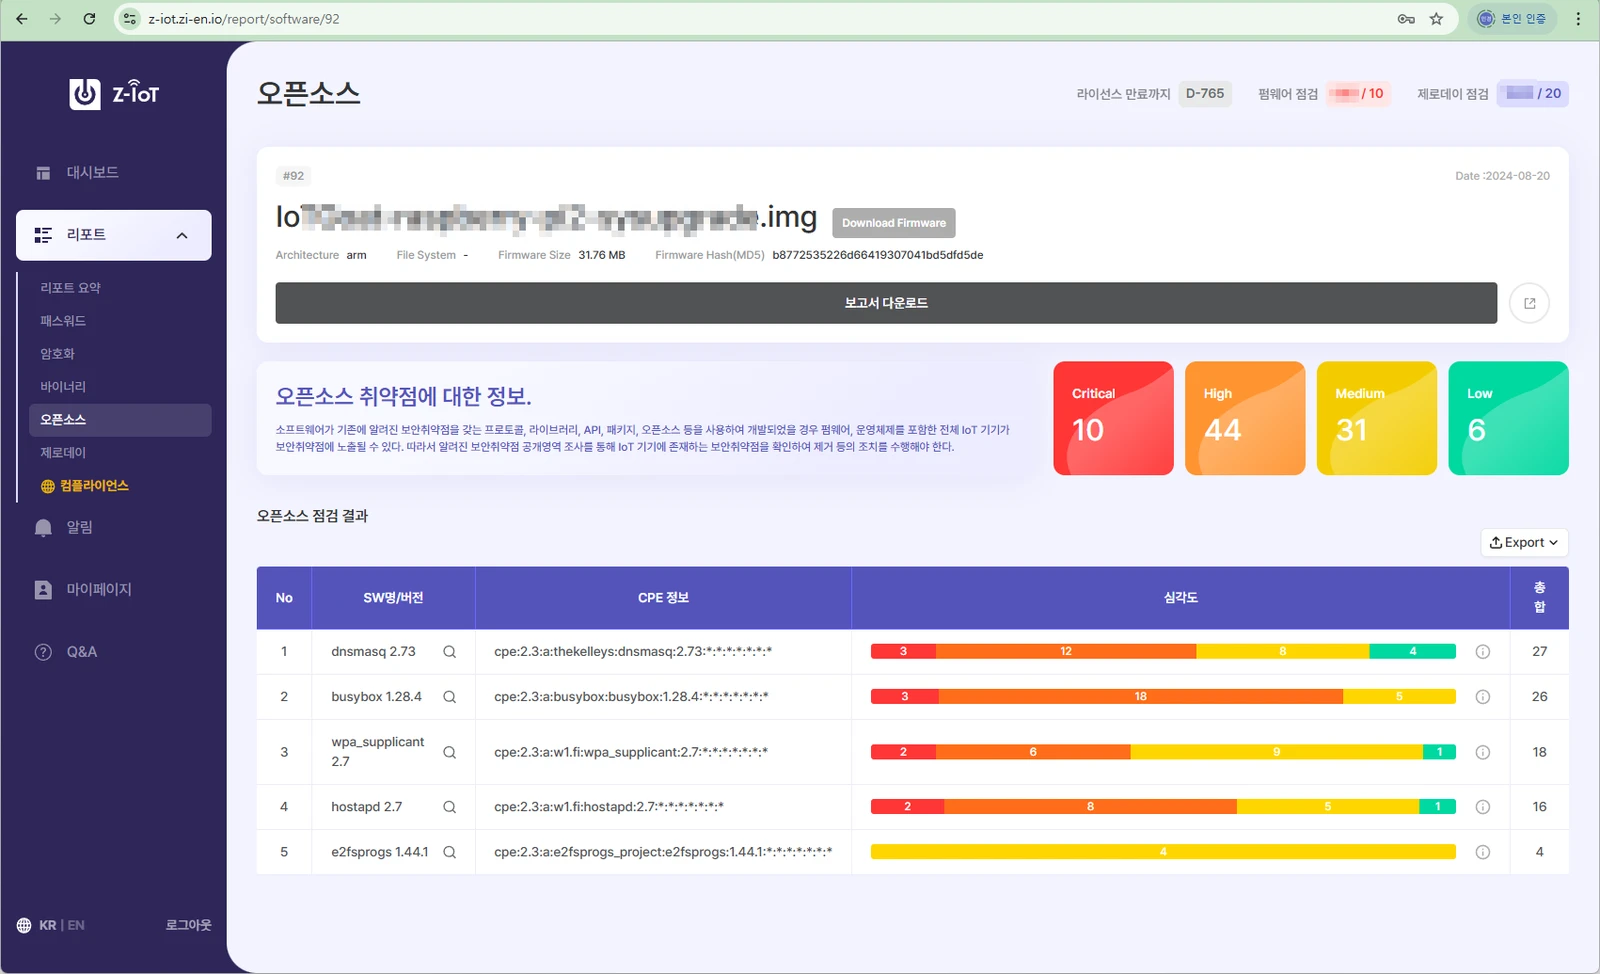
Automated Analysis
Upload a firmware file, and Z-IoT performs static analysis of binaries and file systems to automatically identify open-source and third-party components.
This ensures hidden version details—often missed with manual review—are captured.
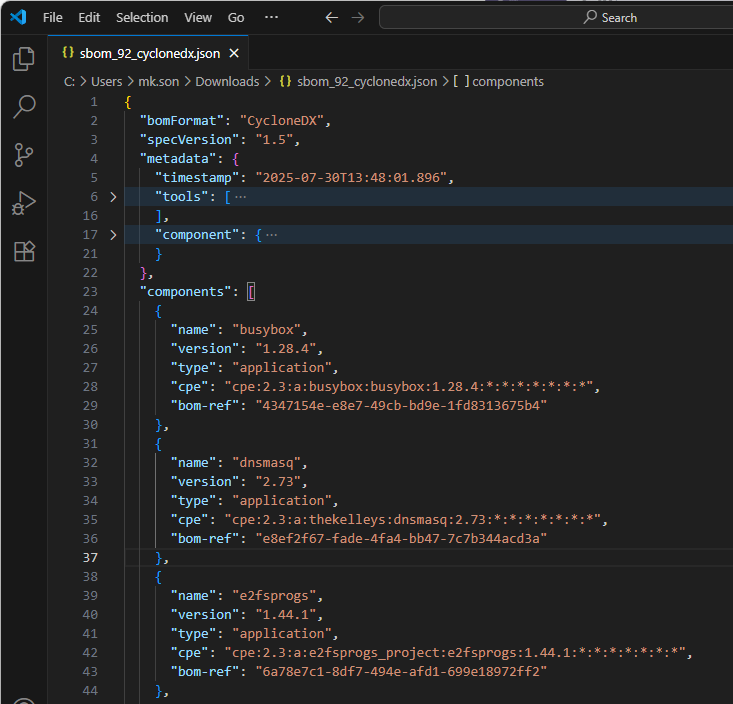
Standardized Formats
SBOMs can be exported in SPDX or CycloneDX formats, making it easy to integrate with existing tools and track component changes over time.
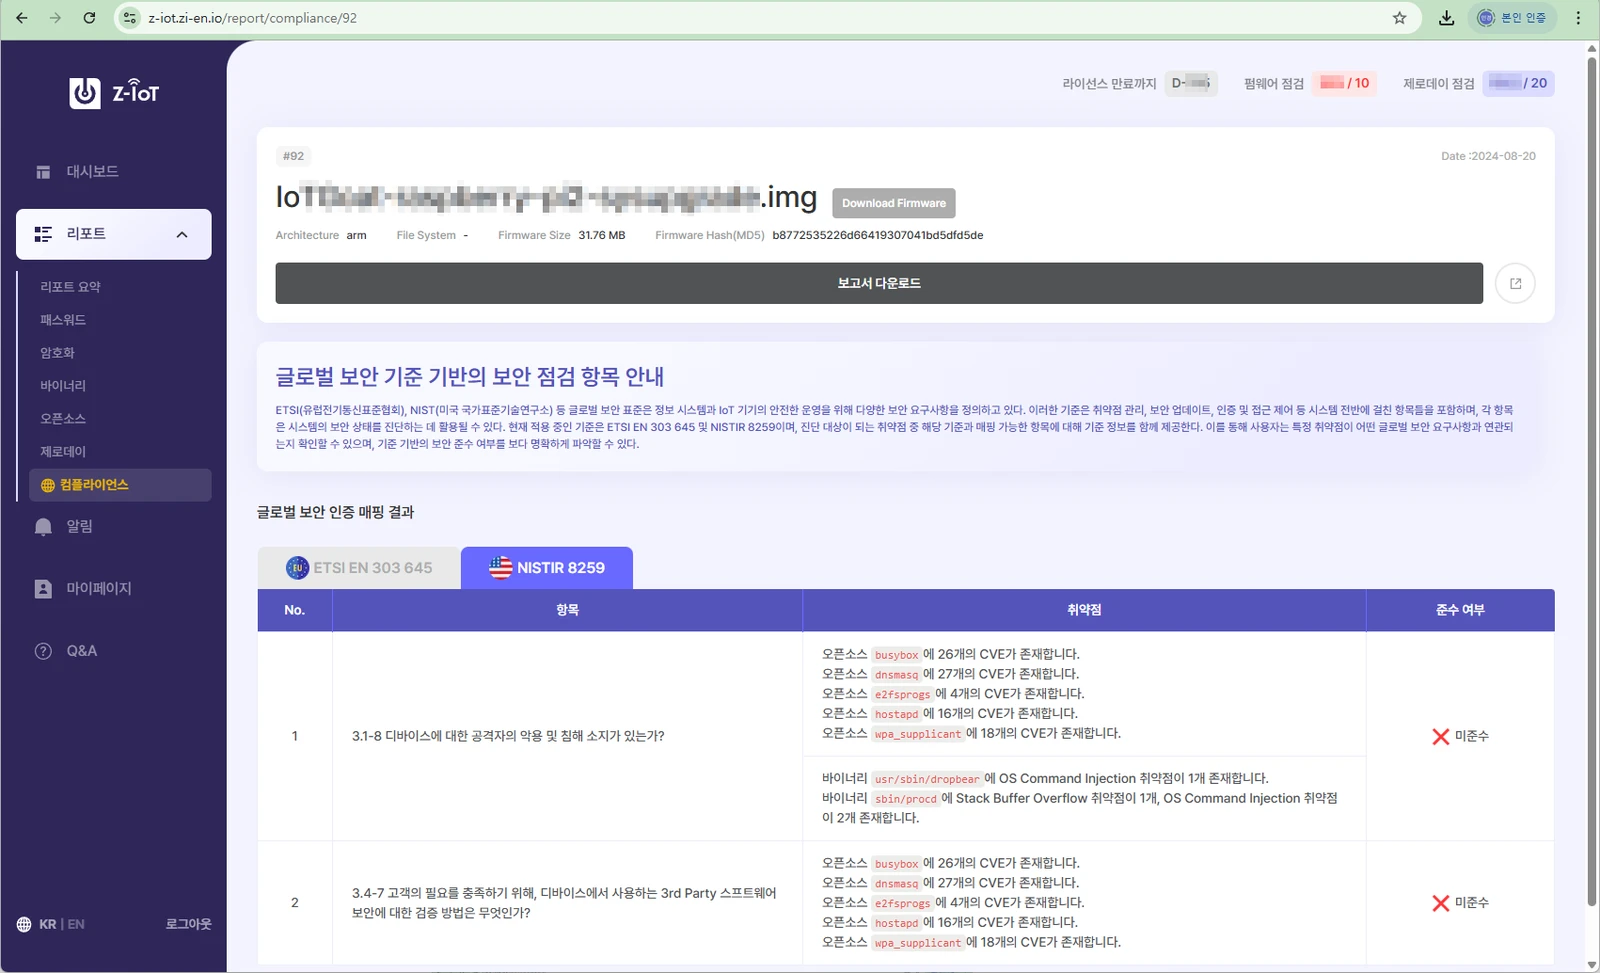
Regulatory Mapping
Z-IoT maps SBOM data against major frameworks such as ETSI EN 303 645 and NISTIR 8259,
helping you quickly verify compliance and prepare for certifications or audits.
By automating SBOM generation in complex IoT environments, Z-IoT takes the heavy lifting off developers and security teams,
making compliance and security management far more efficient.
5️⃣ Proven Reliability and Accuracy
Z-IoT is designed to be more than a basic SBOM generator. It delivers reliable and precise security analysis tailored for IoT.
Real-Time CVE Database
Maintains a continuously updated CVE/CPE database based on NIST, ensuring fast responses without relying on external sources.
IoT-Specific CPE Mapping
Equipped with over 400 proprietary IoT patterns to interpret non-standard strings and incomplete metadata, ensuring accurate component detection.
International Accreditation
Z-IoT has earned KOLAS accreditation, officially validating its analysis accuracy and reliability as an internationally recognized testing and inspection system.
By combining SBOM automation with in-depth component analysis, Z-IoT provides the data you need for secure, compliant IoT product development.
✅ Take the Next Step
If you’re unsure where to begin with IoT security, Z-IoT is here to help.
👉 Contact Us to learn how Z-IoT can streamline your SBOM management and compliance strategy.