In early August 2024, while temperatures in Korea were hitting 35°C with 85% humidity, we headed to Las Vegas for DEF CON 32's IoT Village presentation. The prep work involved tons of research, topic selection, and coordination with the organizers.
Practicing the presentation while waiting for the flight at Incheon Airport
Las Vegas greeted us with its trademark desert heat, pushing 40°C. It felt like someone was following us around with a giant radiator! But the excitement of attending our first DEF CON overshadowed the scorching weather.
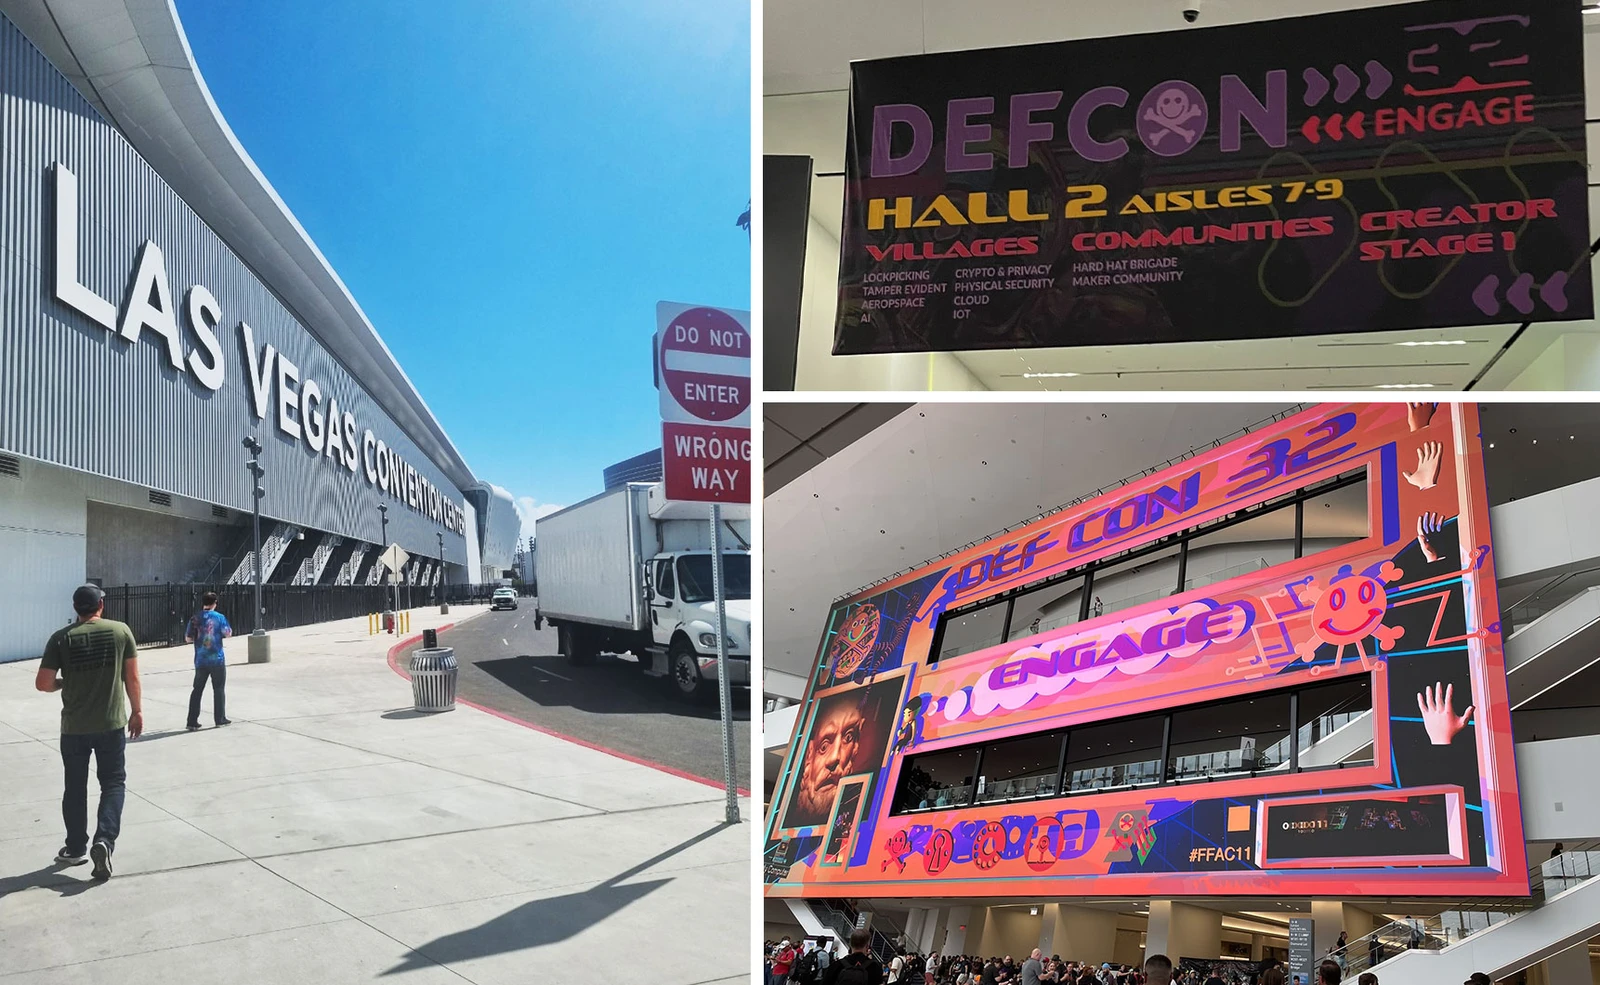
Day one, we made our way to the Las Vegas Convention Center (LVCC) West Hall to pick up our speaker badges. Despite arriving early, the place was already buzzing with long queues for registration. True to its reputation as the world's top security conference, even the merchandise lines were epic. People were snagging all sorts of swag - stickers, tees, caps, bags, tumblers, you name it. Hearing stories of folks waiting seven hours to buy merch really drove home just how popular DEF CON is.
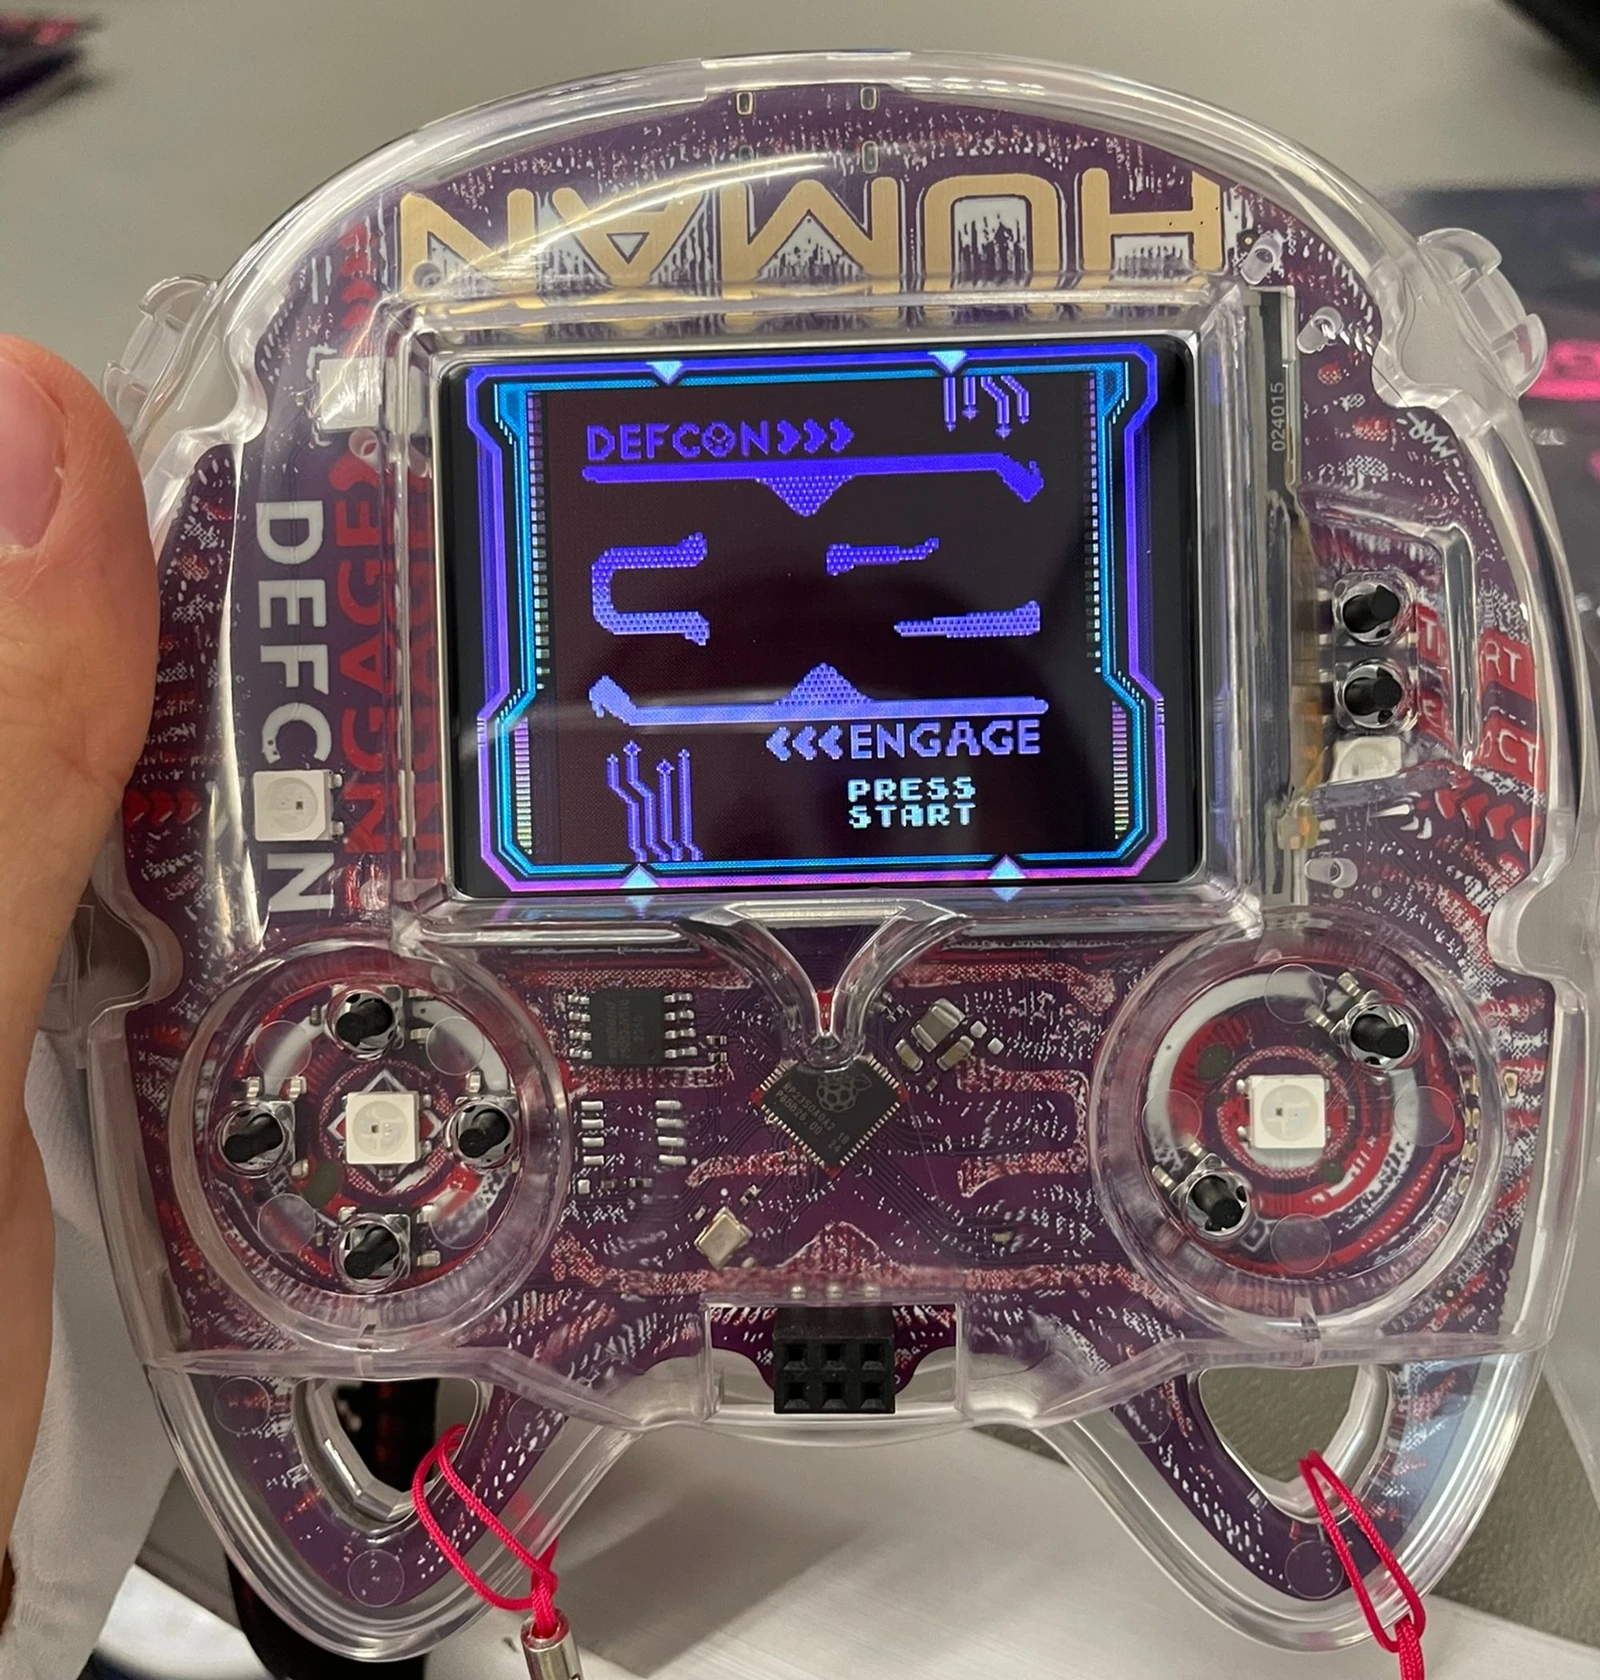
As speakers, we lucked out and got to skip the main queue for our badges. Unlike your typical paper or plastic conference passes, DEF CON badges are miniature computers built on Raspberry Pi. These nifty gadgets came loaded with features - an in-conference map game, options to install other games, firmware updates, and more. They even had dedicated sessions on how to hack these badges! As IoT Village presenters, we scored two free badges, granting us access to all DEF CON activities.
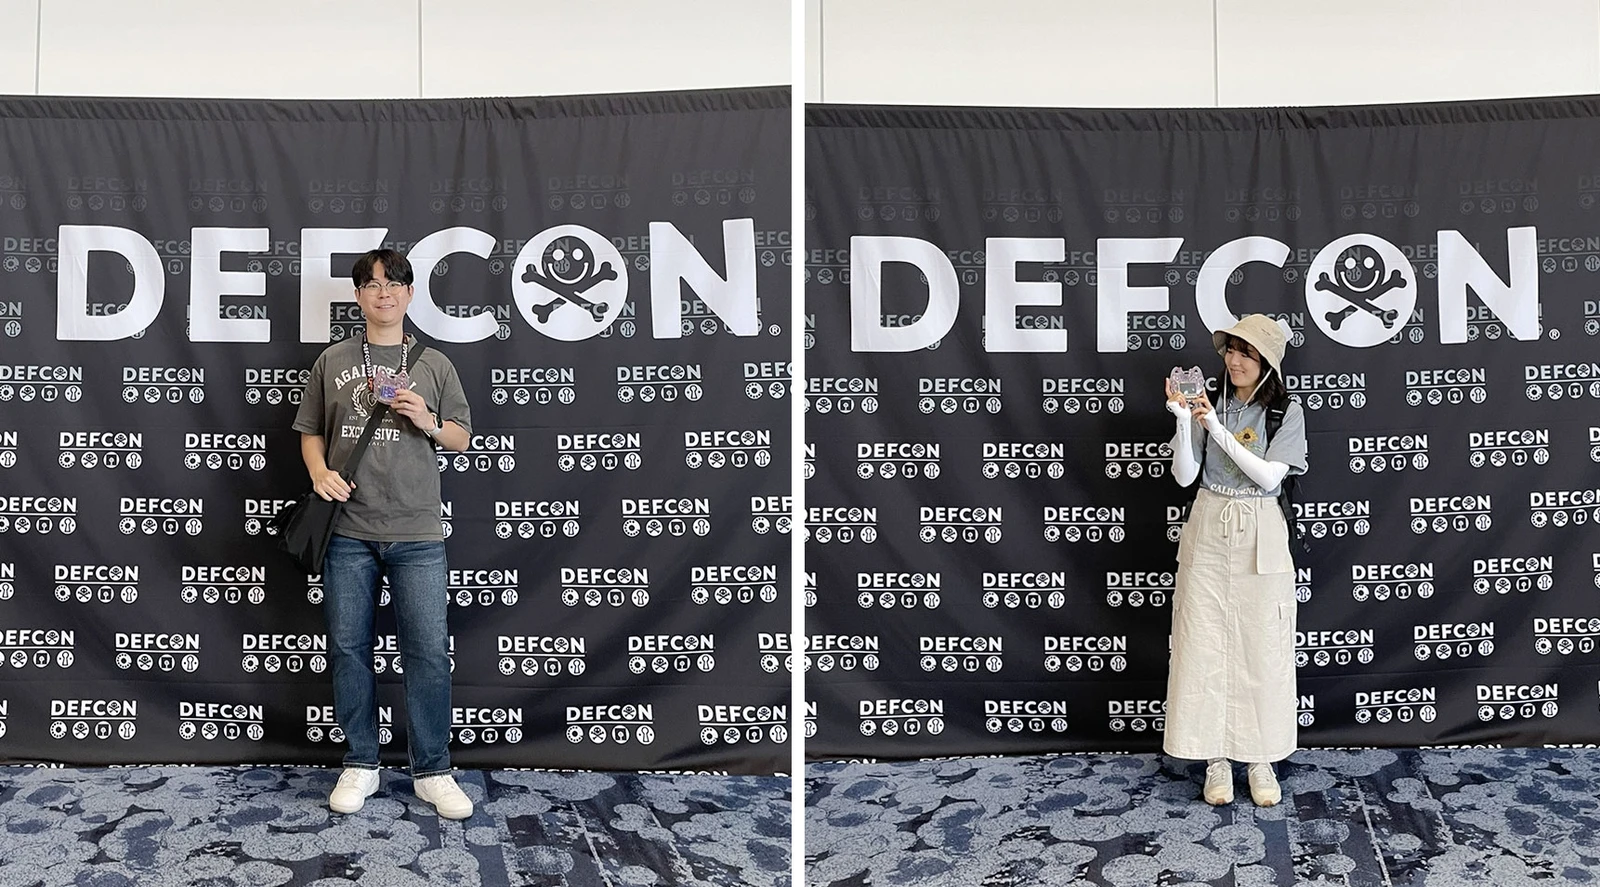
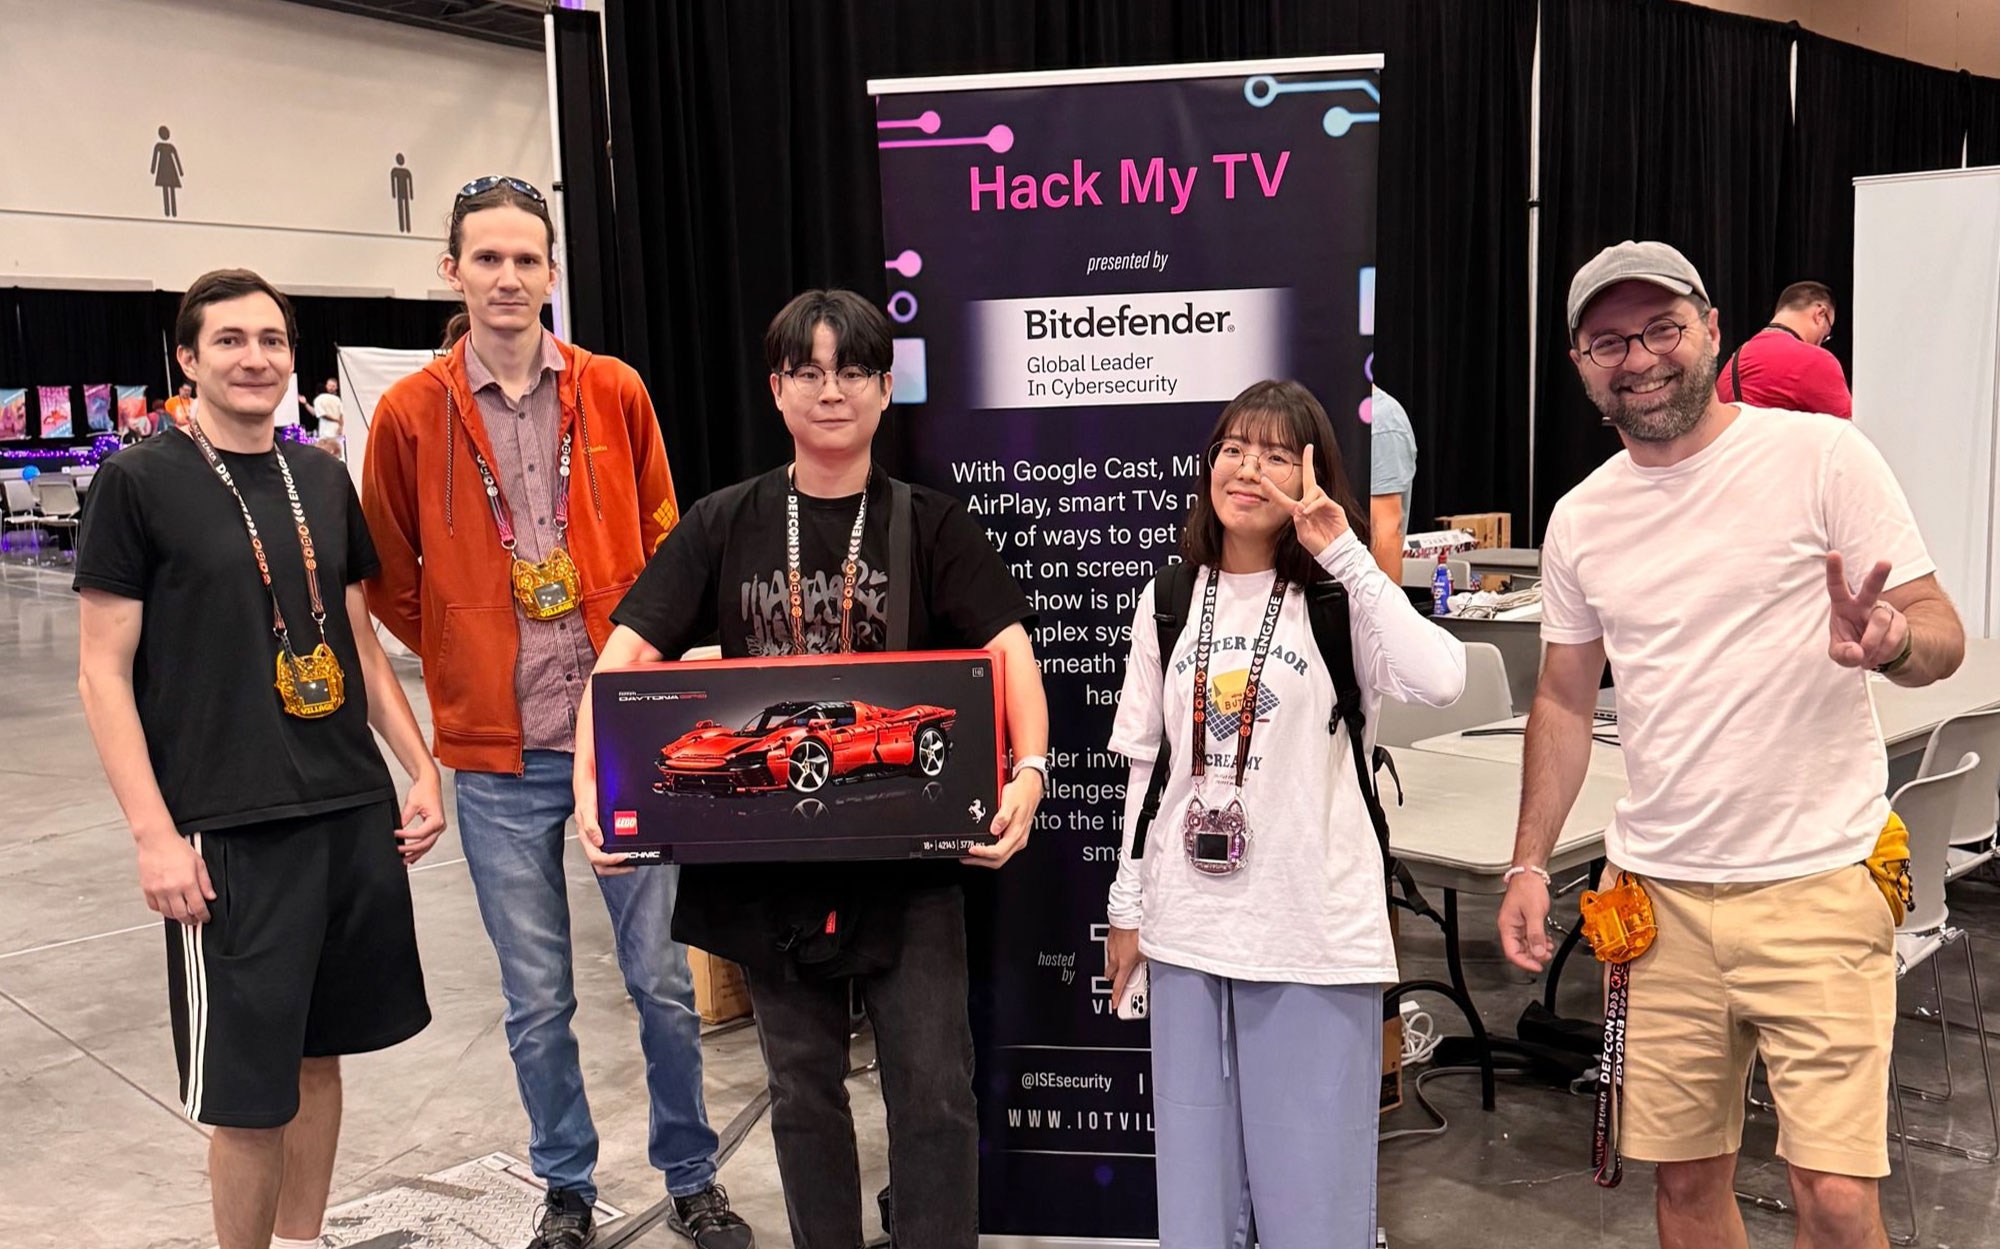
(L)HanRyeol Park, (R)HyoJin Lee
Winning the Hack The TV CTF
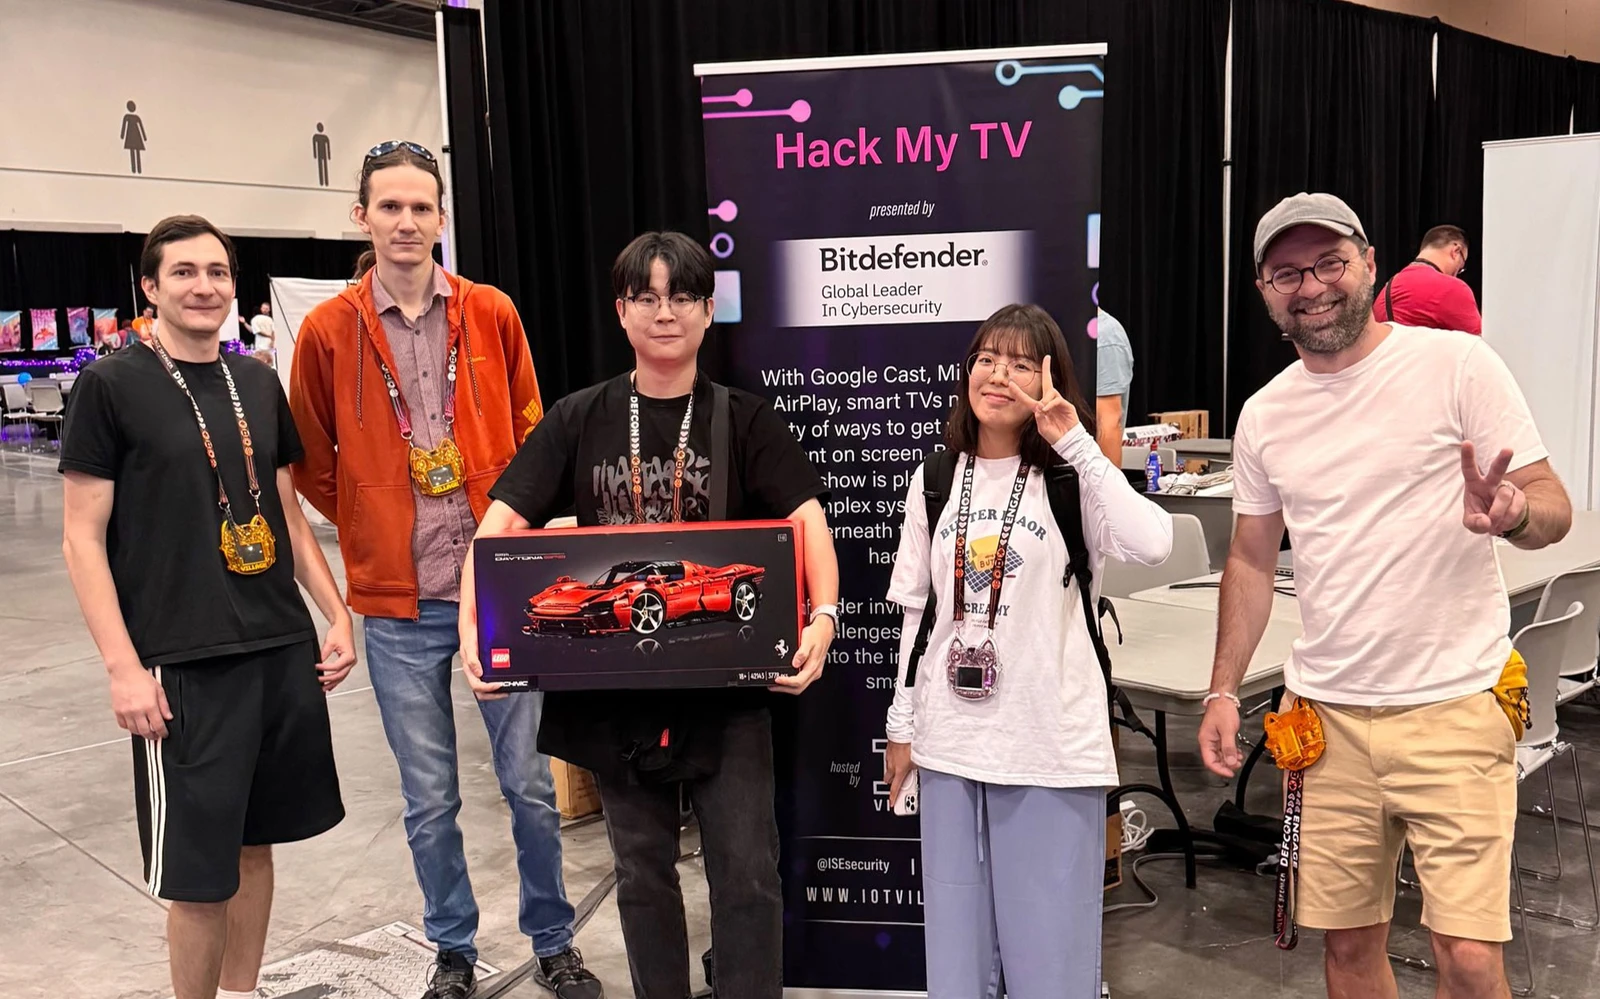
Besides presenting our dashcam security research, we also participated in one of the many hacking competitions at DEF CON - the world's largest hacking and security conference. We participated in the Hack the TV CTF contest in the IoT Village.
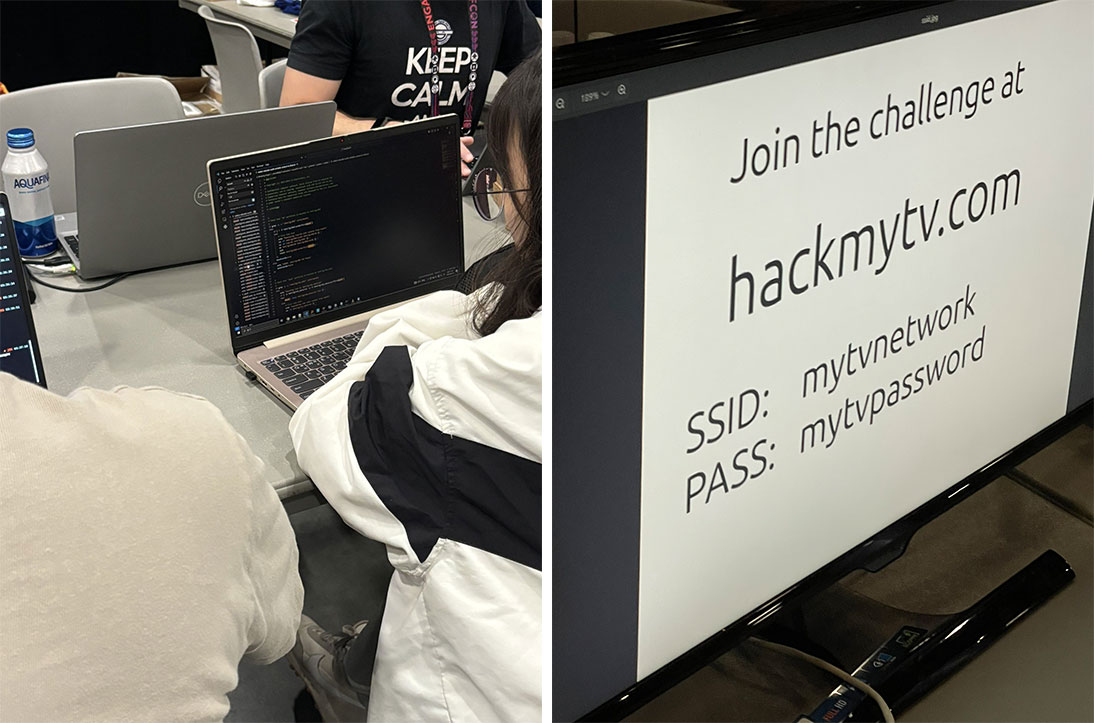
The competition was held using personal laptops, and after connecting to the provided Wi-Fi, participants could access CTF problems on hackmytv.com. There were two problems in each of the four categories: networking, misc, forensics and crypto. Additionally, LG TVs were set up on-site, and there were problems related to those TVs.
When we dug into the provided firmware, we noticed that its structure was similar to the Dashcam research presented at DEF CON. This familiarity helped us speed through vulnerability hunting. We quickly analyzed the initial boot logic and scored points by identifying issues in the firmware update process.
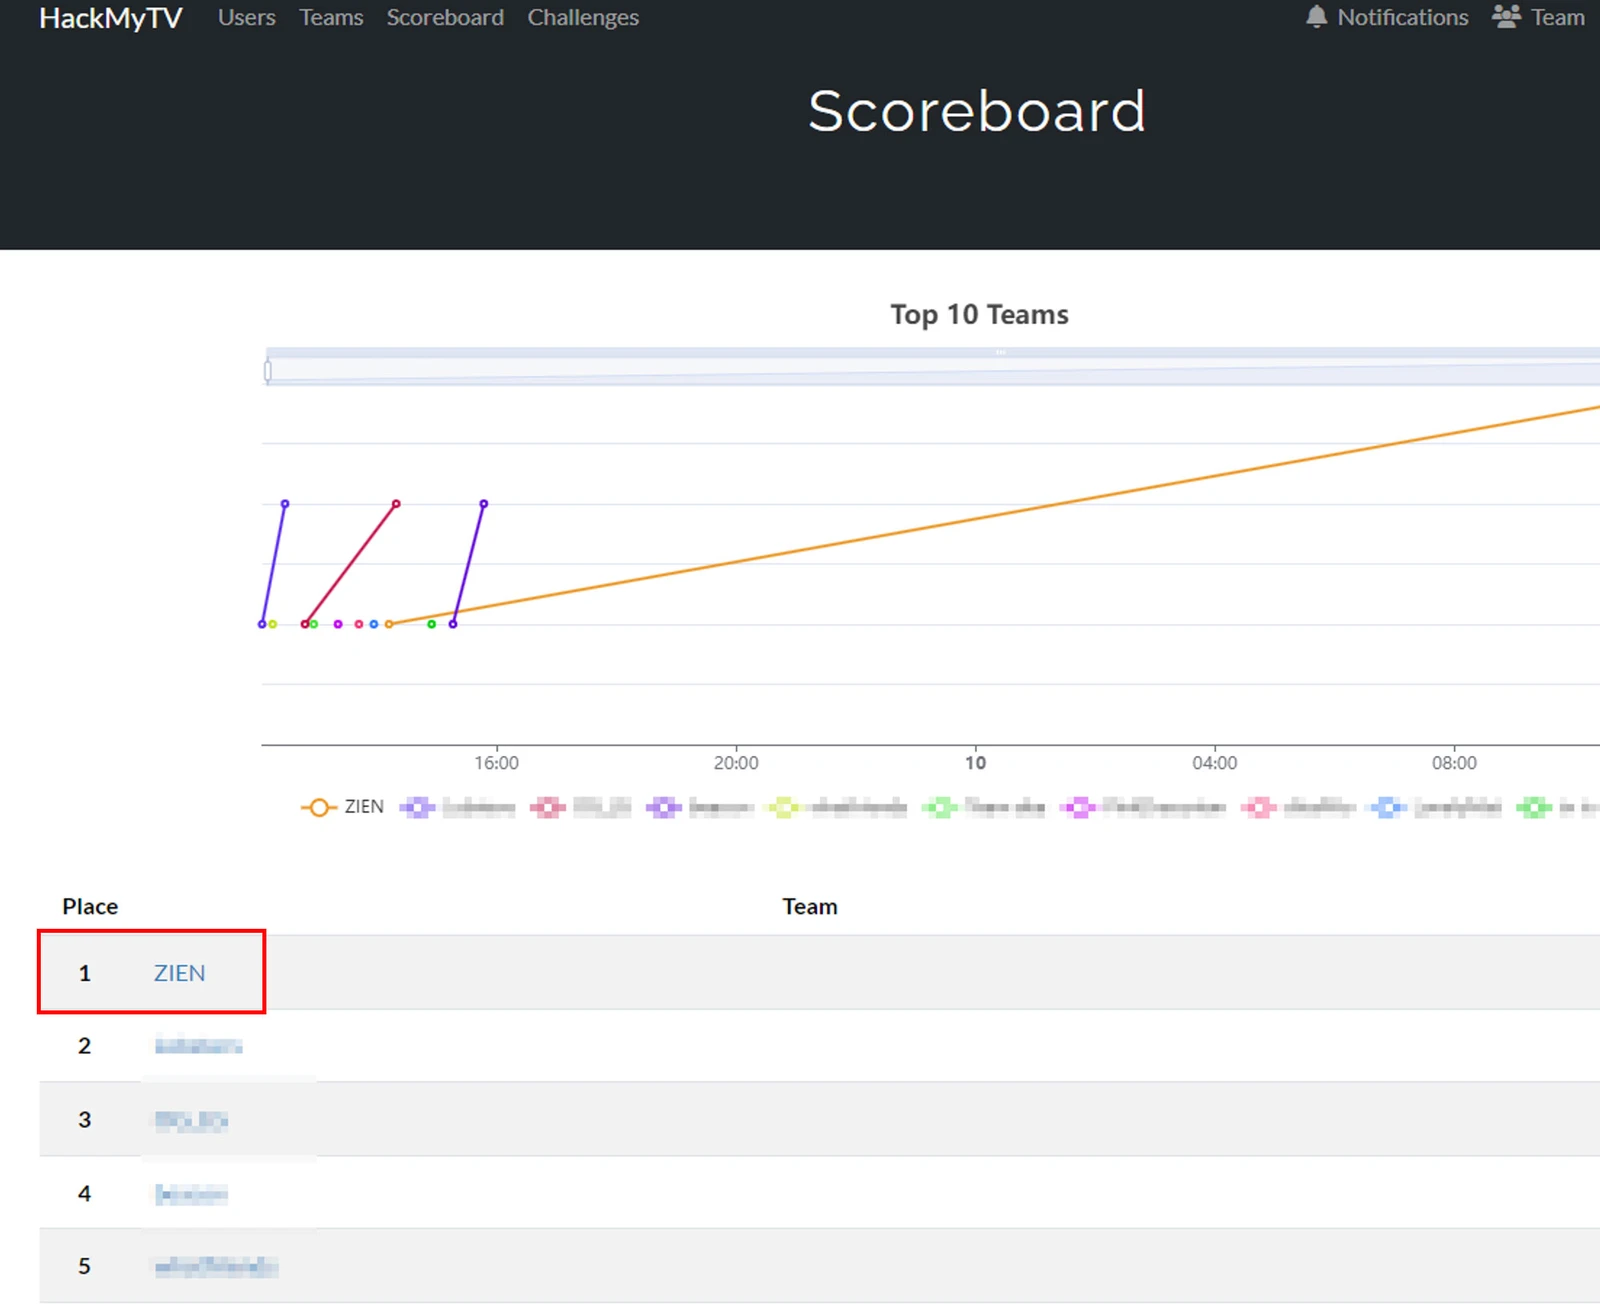
The CTF challenges were based on real CVE vulnerabilities that the organizing security team had discovered while analyzing LG Smart TVs. Each problem was derived from interesting aspects of the hacking process for the TVs, and the difficulty level was very high. Out of 30 teams, only four teams managed to solve the actual problems, highlighting the challenge. However, it felt rewarding to engage in the process of hacking a TV, making the experience enjoyable.
Conference
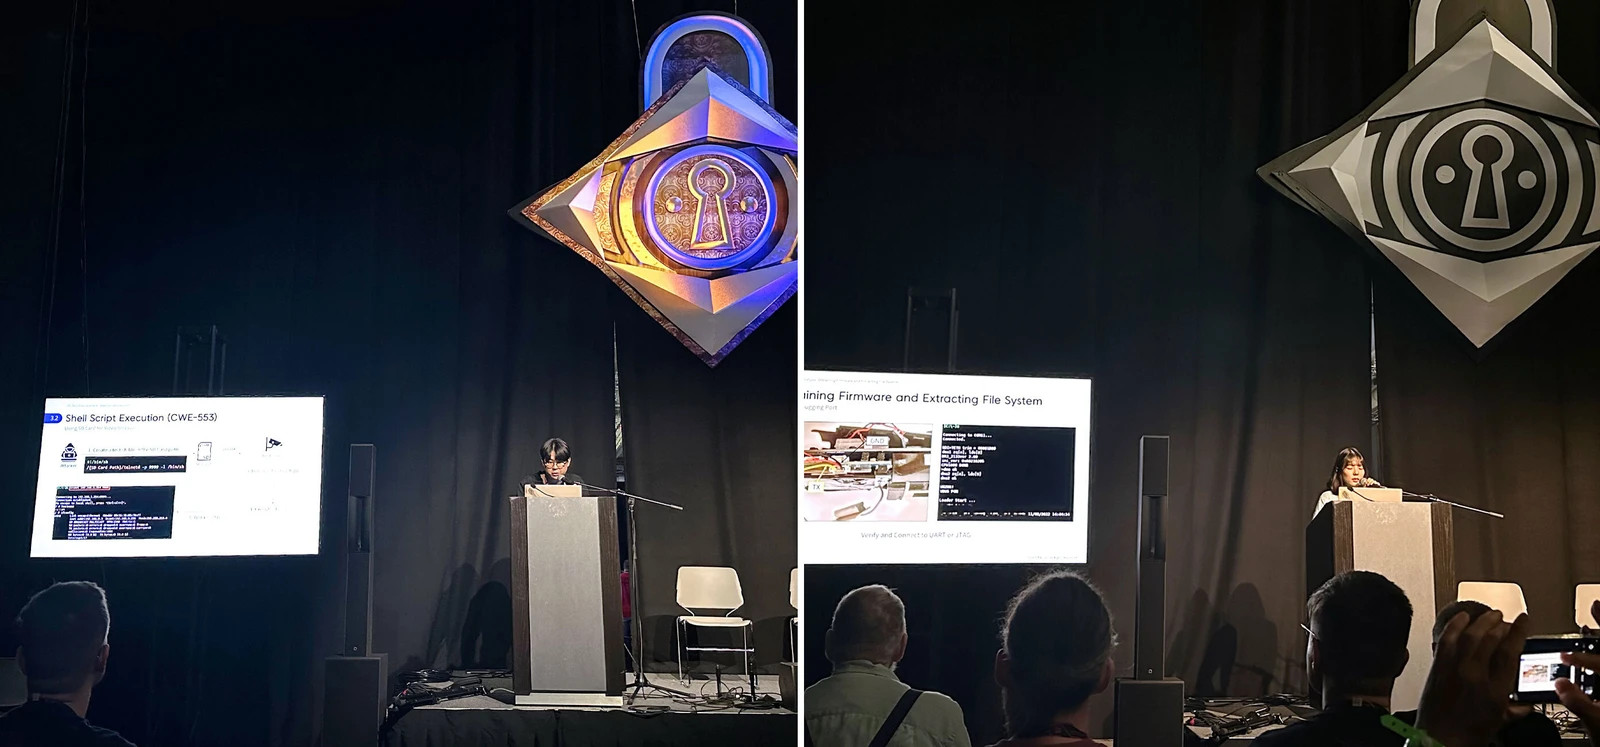
In addition to the CTF, our team's experience presenting research on Dashcam vulnerability analysis methods and 0-Day vulnerabilities at DEF CON was impressive. The presentation took place at Creator Stage 2, where many people gathered with interest to share our research, creating a valuable opportunity. For more details, please refer to the blog post [Interview] ZIEN R&D Team Presents Dashcam Security Research at DEF CON 32's 'IoT Village’.
The various presentations at DEF CON are one of the key events, with a total of 106 main presentations and 114 at Creator Stage. Additionally, there were presentations by Village members and those who submitted CFPs held in various locations. Topics included the exploration process of 0-Day vulnerabilities, which can be considered the "flower of security," as well as recent security threats utilizing 1-Day vulnerabilities. Recent global issues such as OSINT, SBOM, LLM, and AI were also covered. I would like to briefly introduce two presentations related to the latest issues.
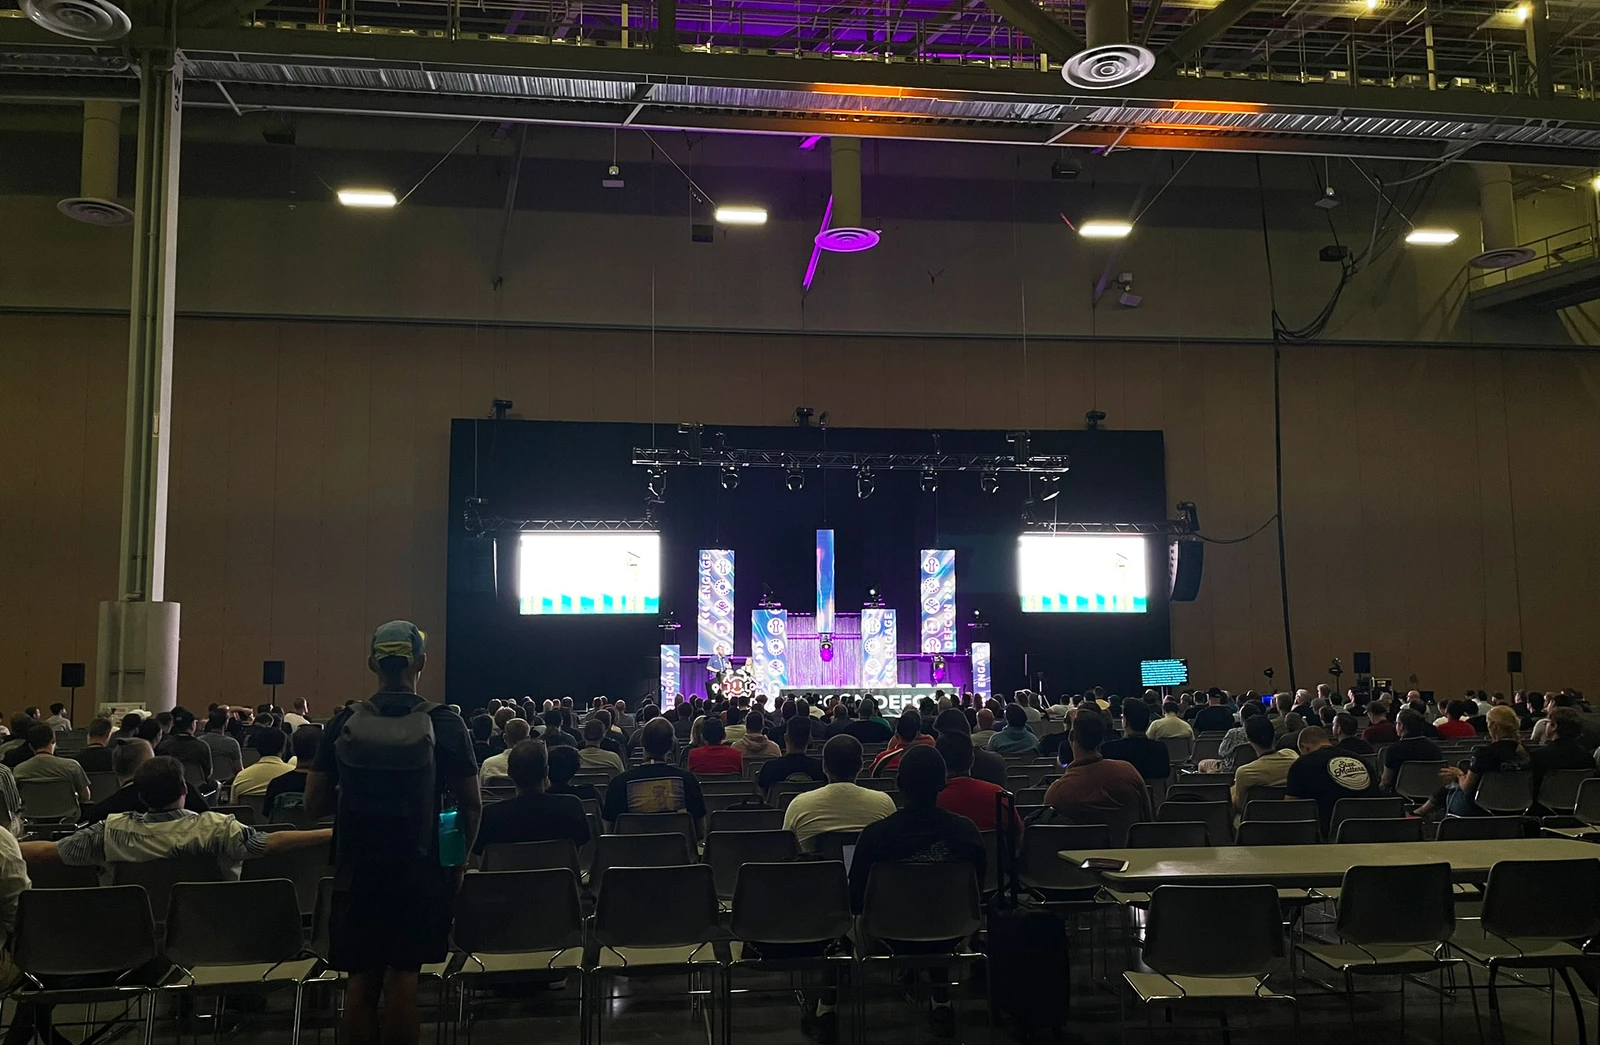
The first presentation was titled "Recursion is a Harsh Mistress: How (Not) To Build a Recursive Internet Scanner," related to the well-known recursive OSINT tool BBOT. This presentation was given by thetechrOmancer, the creator of BBOT, who explained the challenges and precautions encountered during the development process aimed at improving BBOT's performance. A crucial consideration when creating recursive OSINT tools is to avoid tracking unnecessary URLs (like JS, PHP, etc.). The presentation also introduced methods to prevent infinite recursion. From this presentation, I realized that an OSINT automation tool conceived in the past could be built similarly, and if the visualized results are presented in a user-friendly manner, it would be extremely useful for analysts.
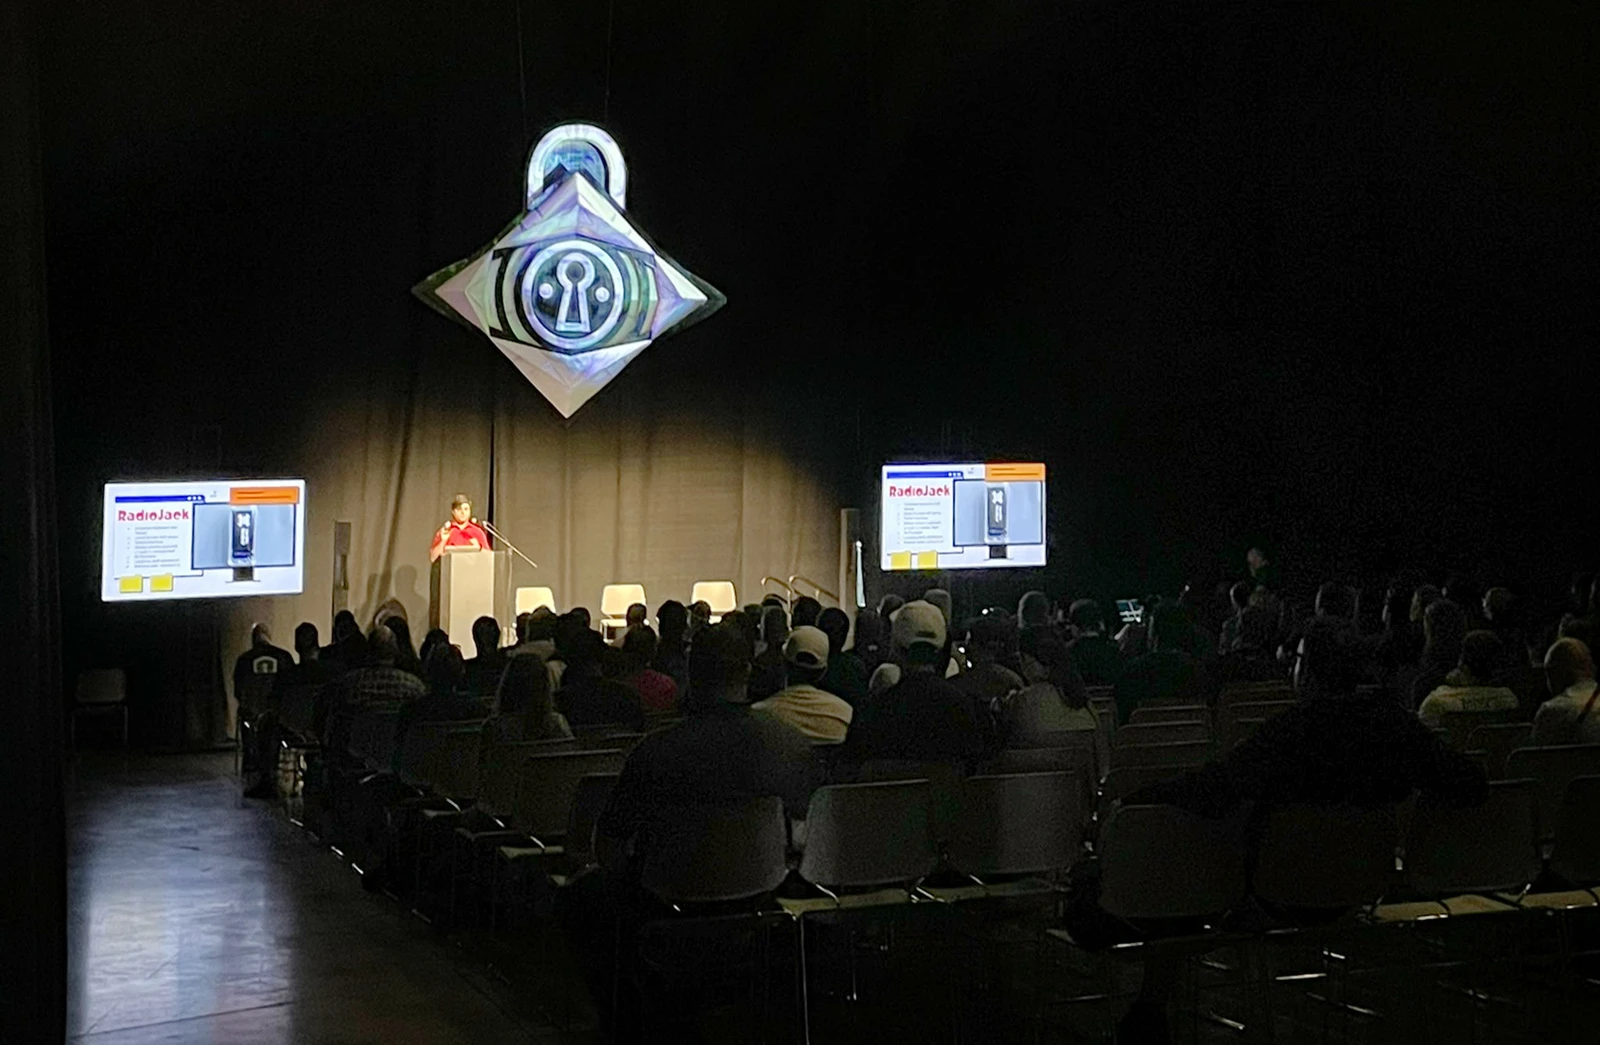
The second presentation was titled "SBOMs the Hard Way: Hacking Bob the Minion," which detailed the process of hacking the Bob the Minion WiFi router from Davolink using SBOM. The presenter extracted and recovered encrypted firmware using SPI Flash and JTAG/SWD interfaces, then found vulnerabilities in open-source software through SBOM, reporting the security vulnerabilities discovered. Since this router was based on the Minions characters, it felt even more amusing as the presenter bore some resemblance to them.
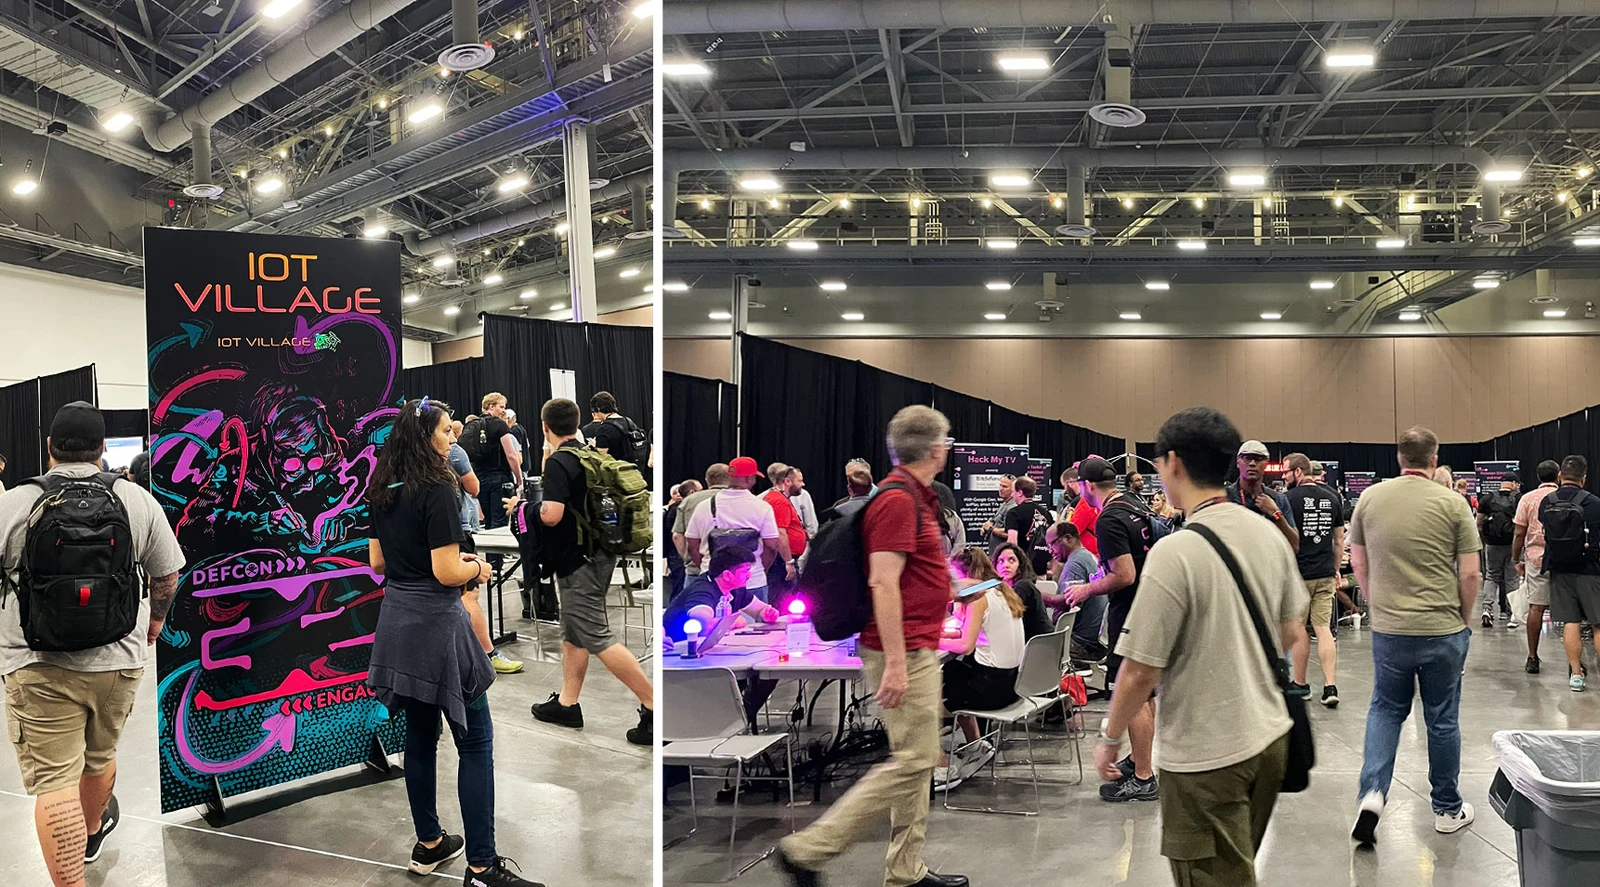
In addition to these, DEF CON offered various experiential events. There are about 30 Villages at DEF CON, including AI, Red Team, Blue Team, and Cloud, each hosting events and presentations such as CTFs and workshops tailored to their fields. Among the many Villages, we focused our exploration on the IoT Village.
Hardware Hacking Contest Review
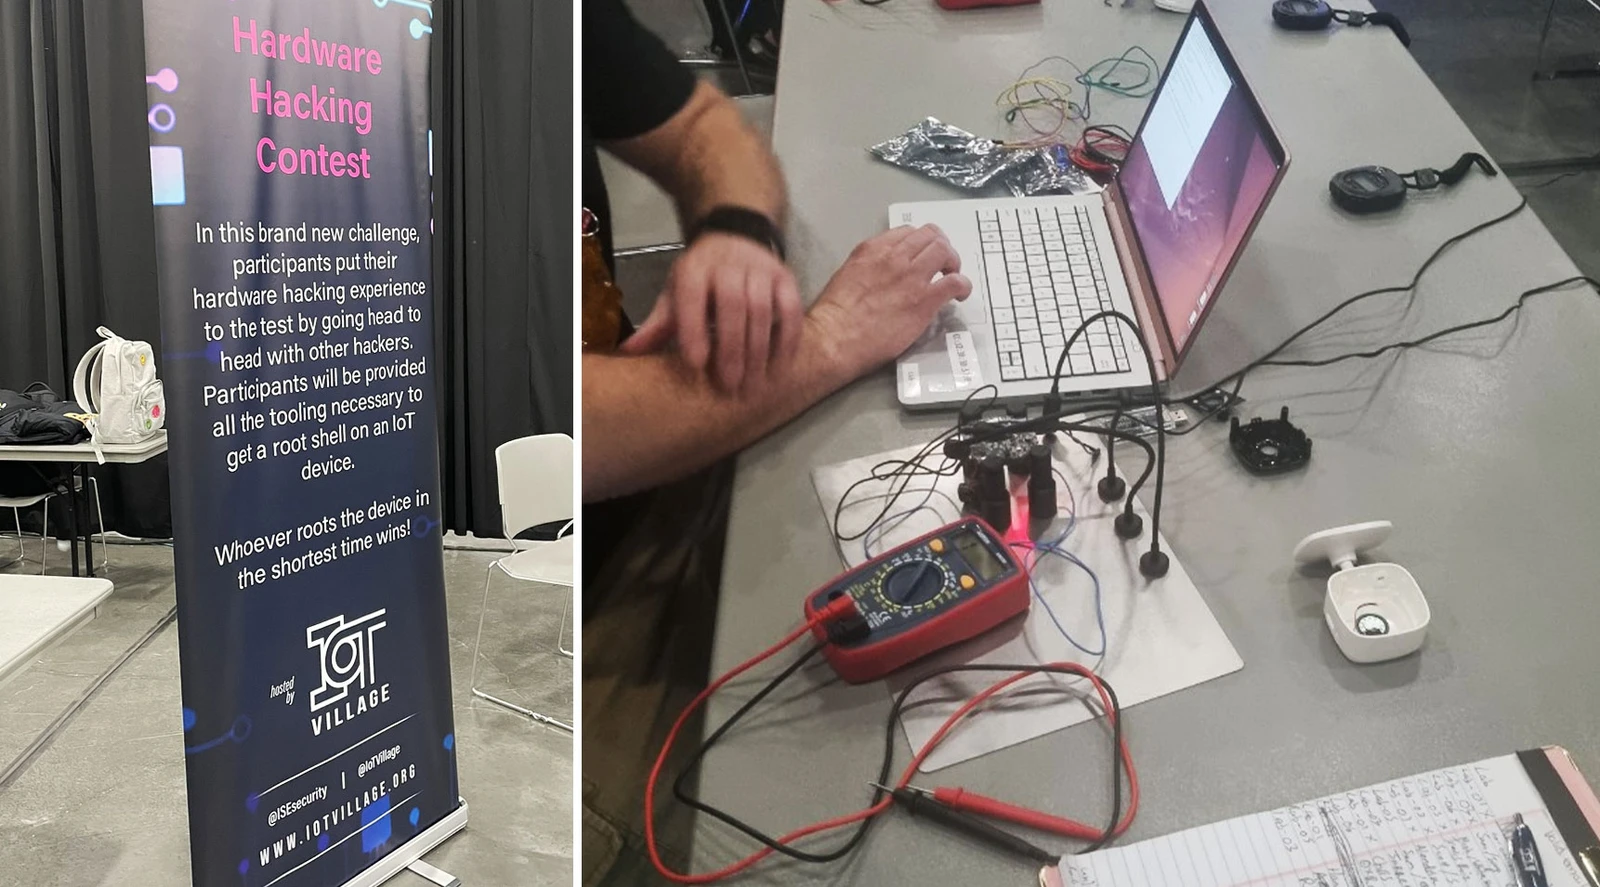
The Hardware Hacking Contest, part of the IoT Village event, involved obtaining a shell from three disassembled Tapo C100 camera circuit boards using a provided laptop, multimeter, Tigard, and other equipment. The time taken to acquire the shell was the criterion for determining the winner, and there were no specific participation requirements, although participants needed an available spot. The provided laptop had only basic tools installed, such as firmware, minicom, screen, and Ghidra, and there was no internet connection, so necessary searches had to be conducted via a mobile phone.
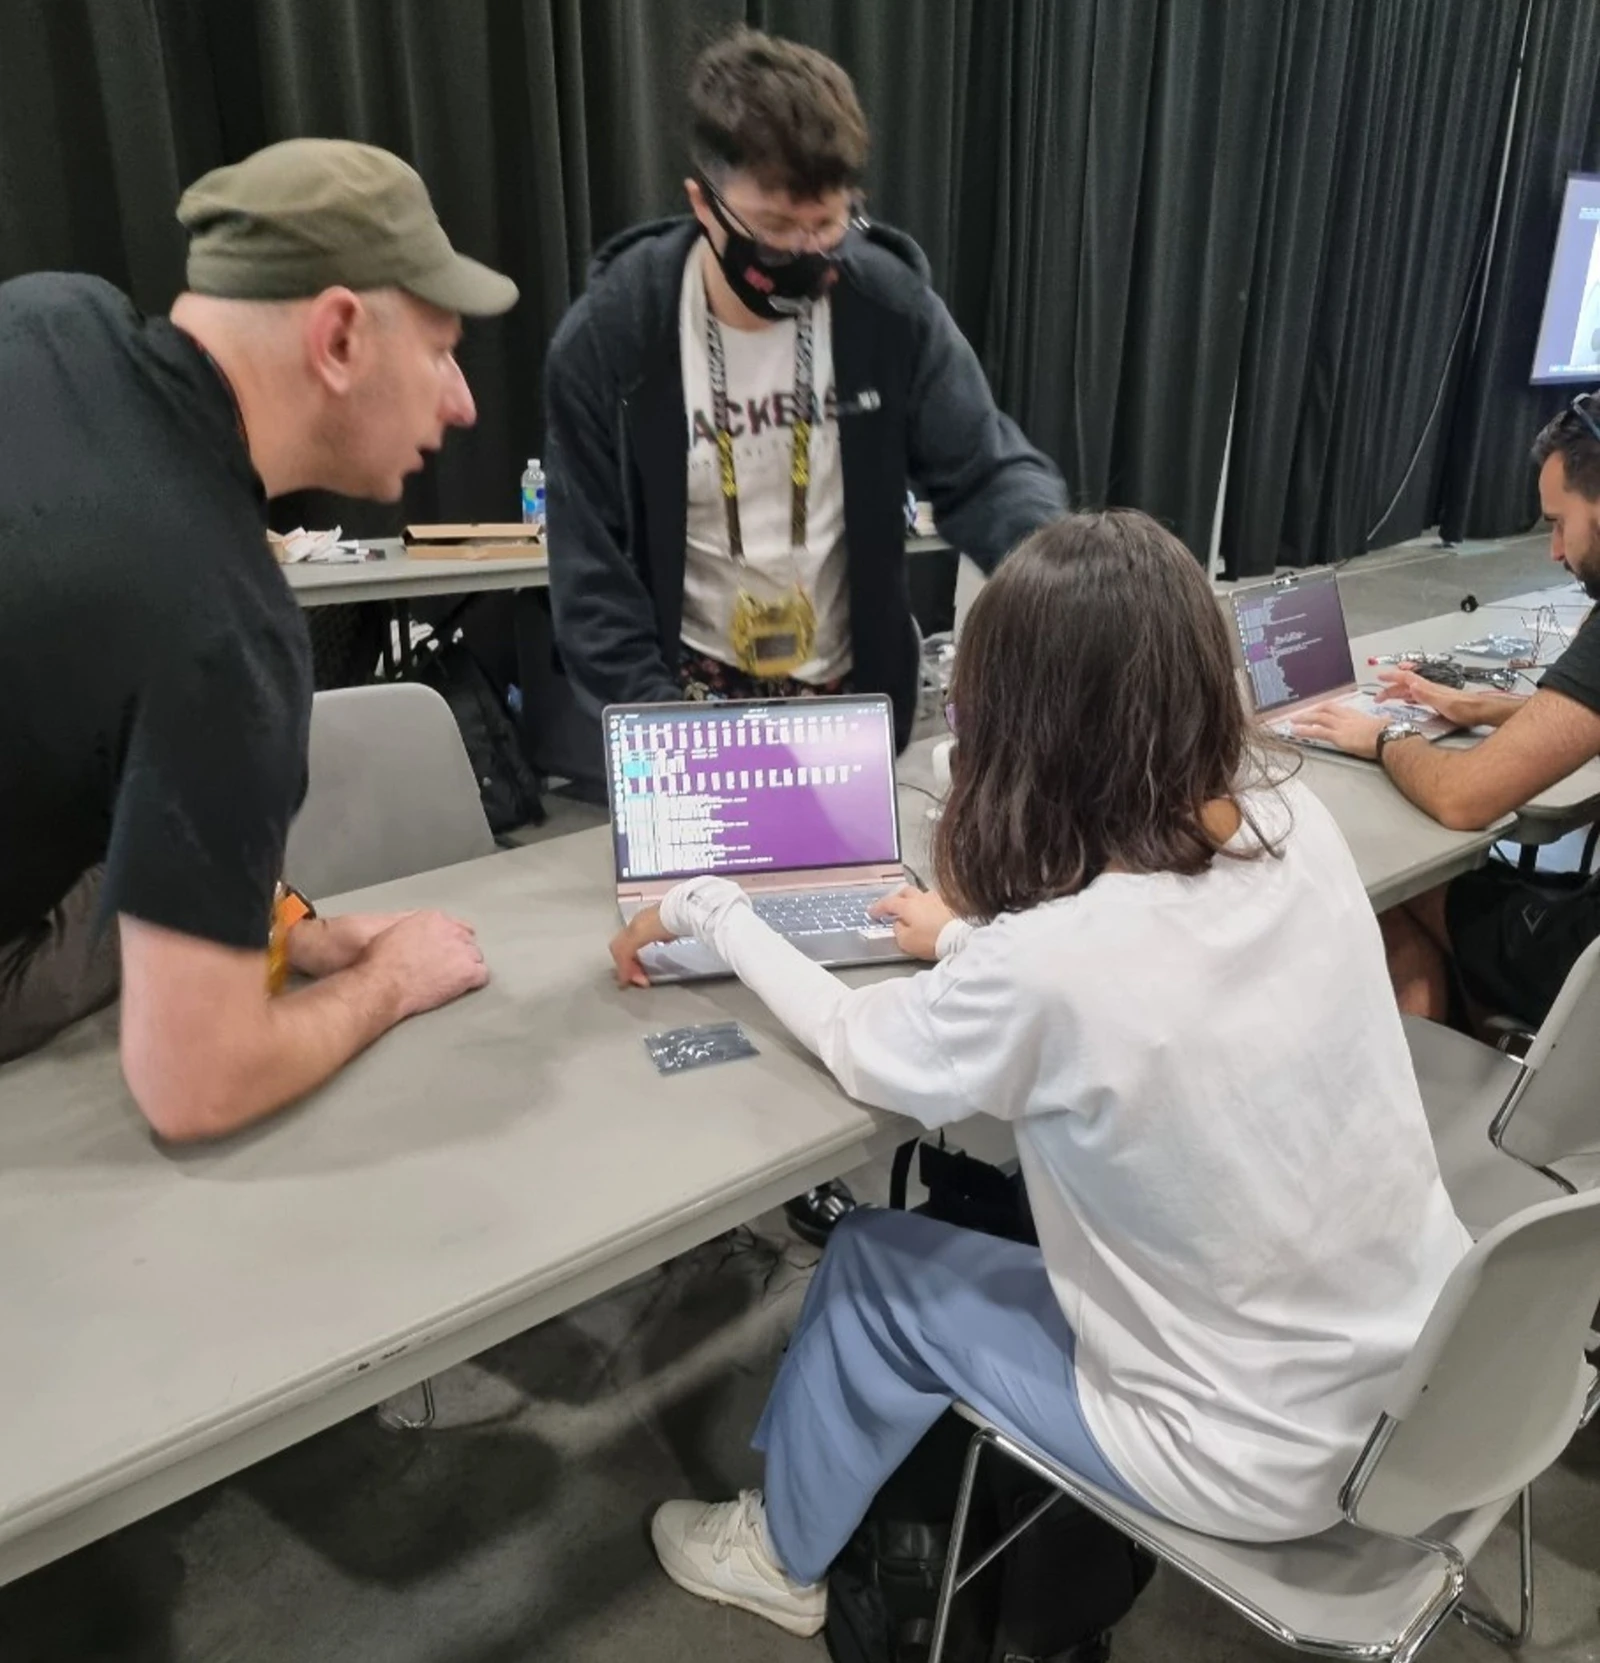
Sharing with the staff that the tty is not recognized
Although the contest had ended on the last day of the conference, we decided to challenge ourselves for fun. We discovered a UART connection on the circuit board and identified the tx and rx pins, then connected via USB using Tigard. However, the tty was not recognized, so we requested a cable replacement from the staff, and it was subsequently recognized as /dev/ttyUSB0.
# screen /dev/ttyUSB0 115200
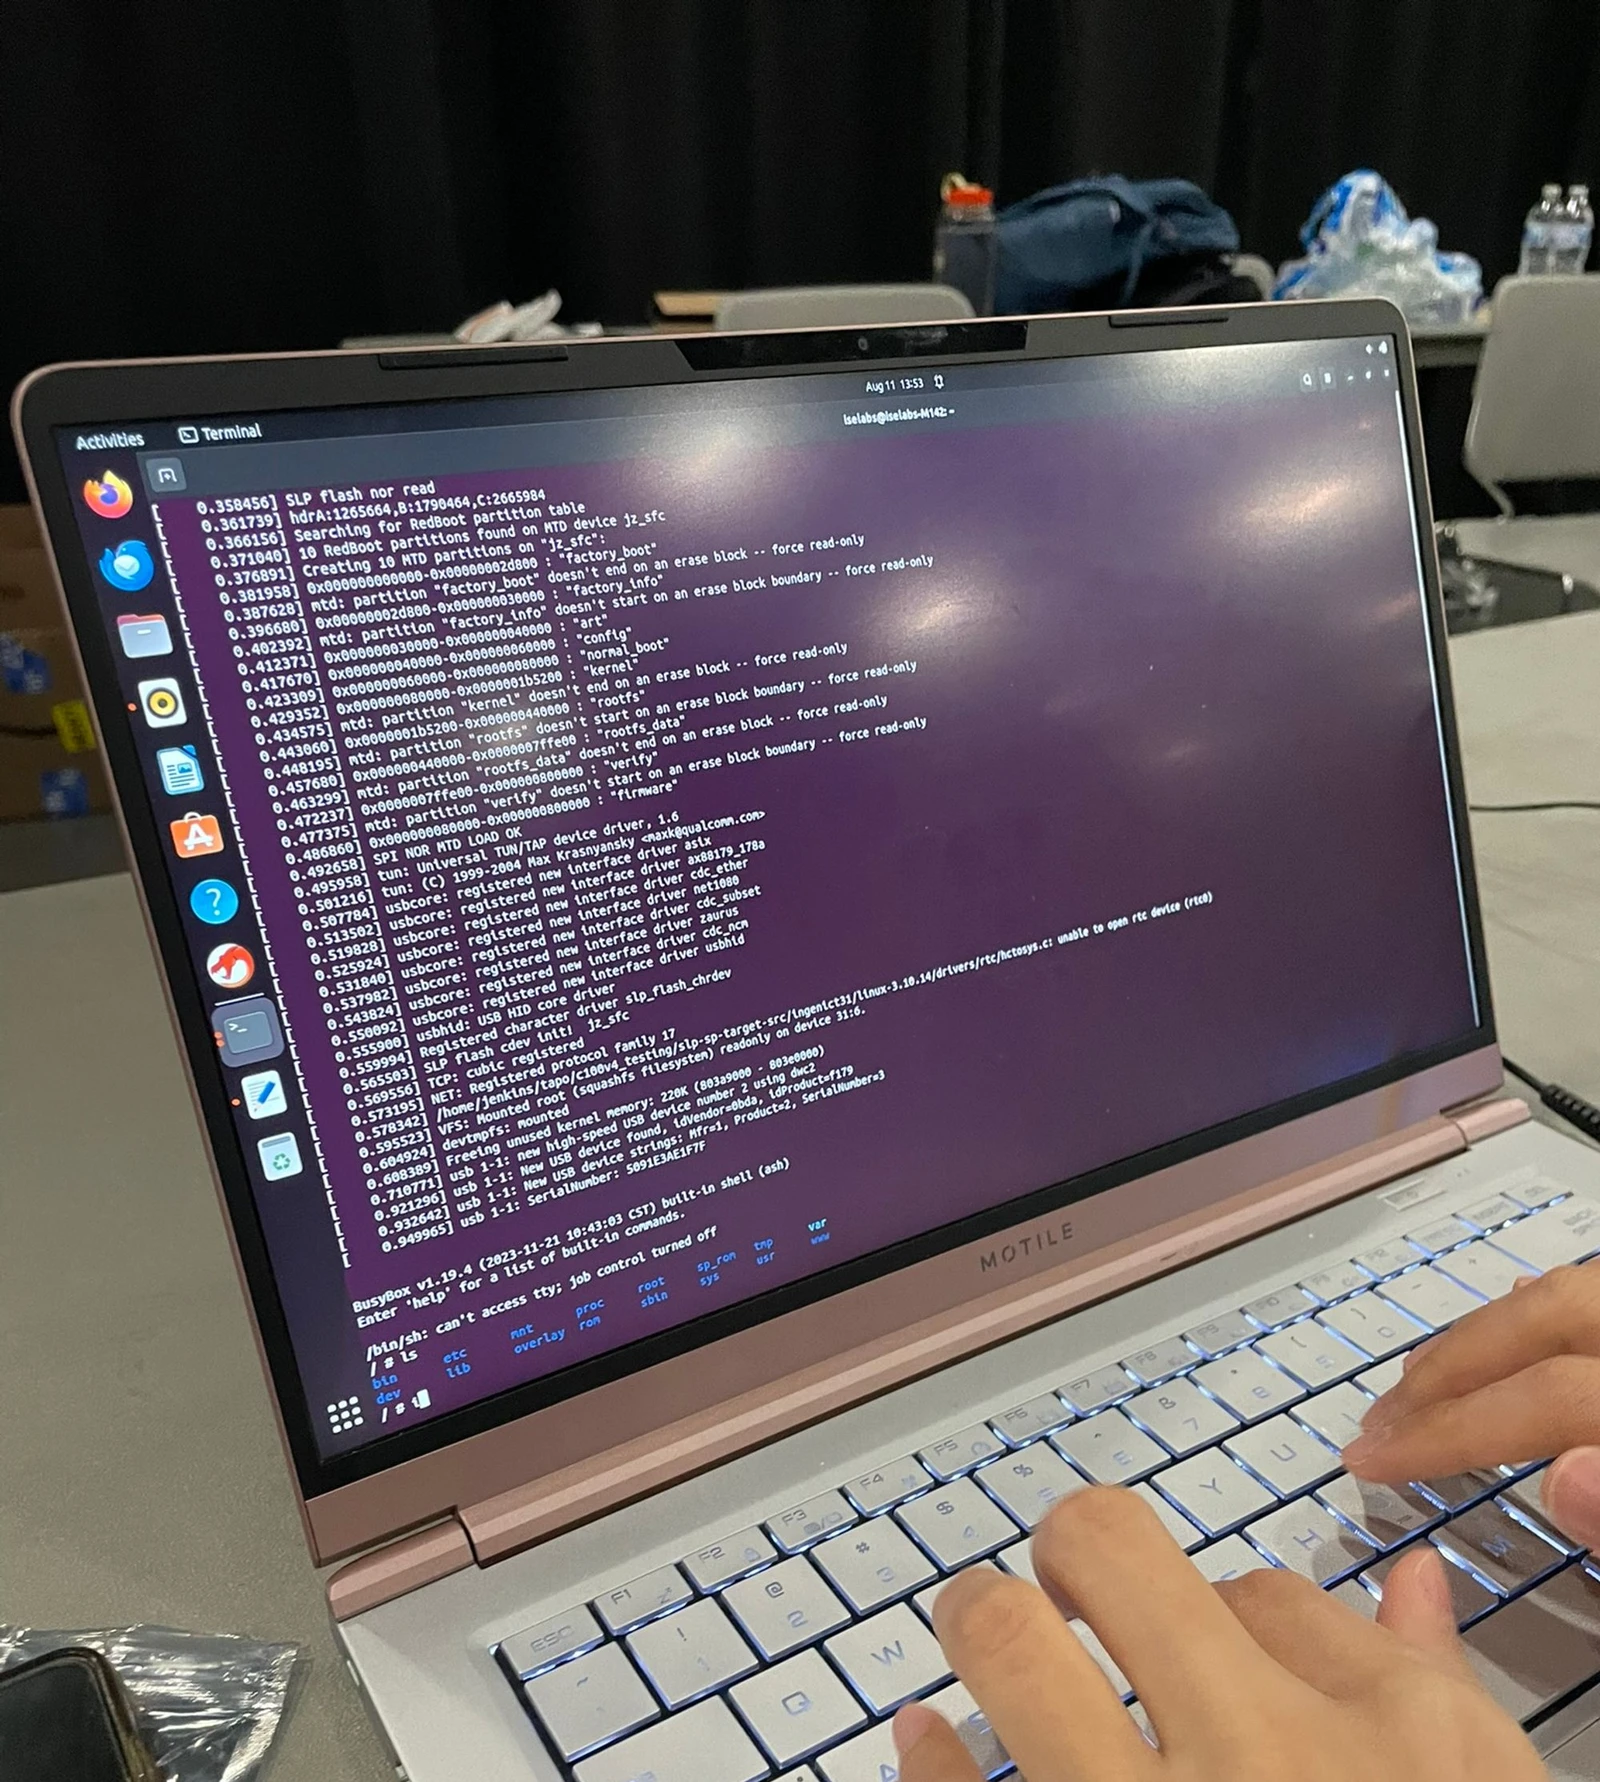
Successfully obtained the shell
We could not immediately obtain the shell, as a login was required. Analyzing the firmware with Ghidra revealed that pressing the S + P + L keys would allow us to enter the bootloader. After powering off and on, we pressed the S + P + L keys to enter the bootloader, and successfully acquired the shell with the next command.
isvp_t30# setenv bootargs ~~~ init=/bin/sh
isvp_t30# setenv bootcmd sf read 0x80700000 0x80200 0x175000
isvp_t30# saveenv
isvp_t30# bootm 0x80700000
Finally, we'd like to recommend two restaurants for those visiting Las Vegas to attend DEF CON.
Denny's
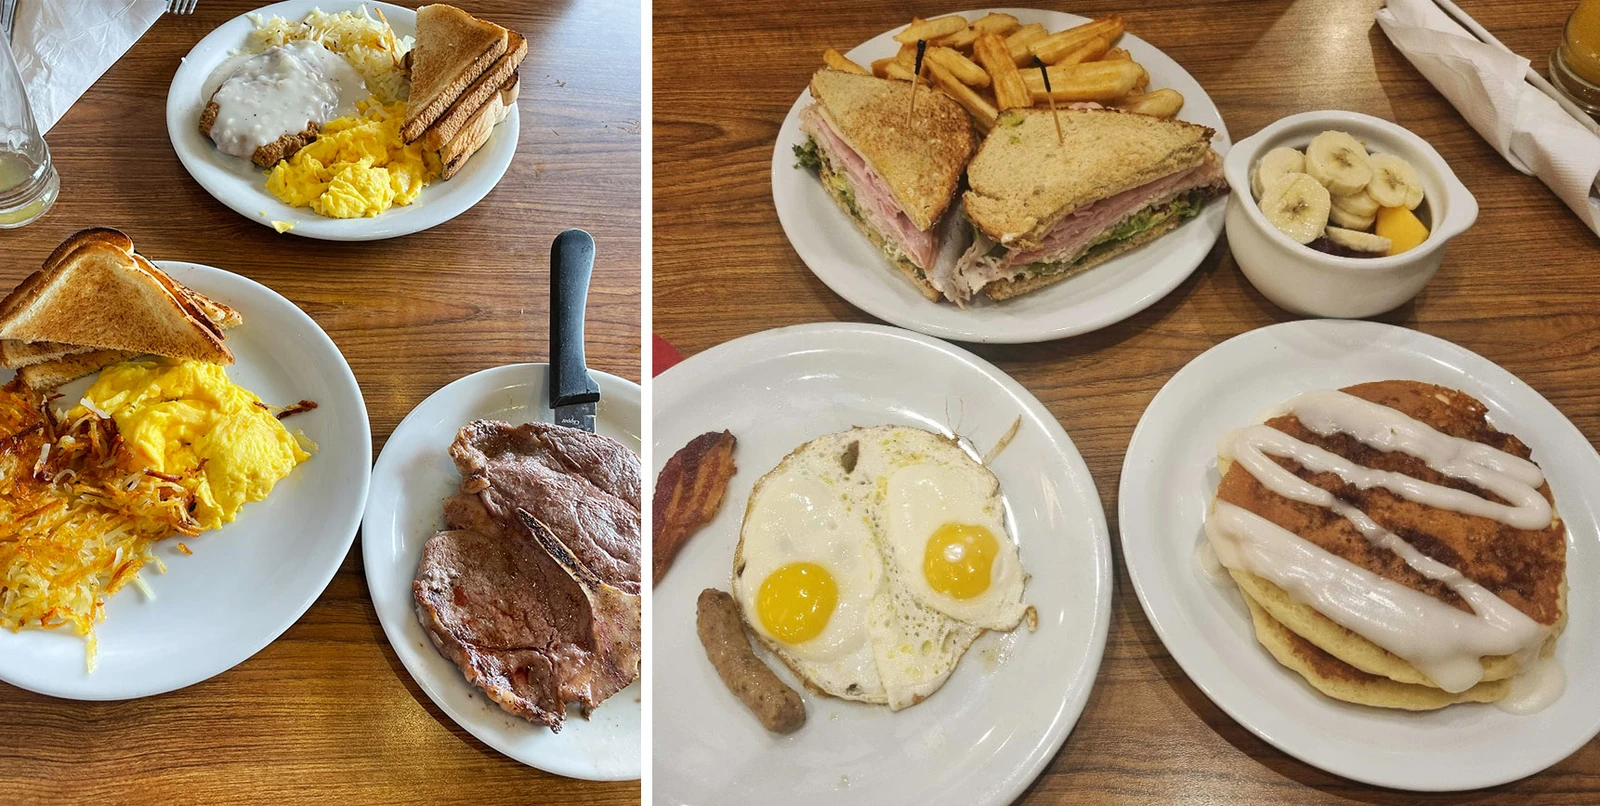
The first place we recommend is Denny’s, located right in front of the West Hall of the LVCC where DEF CON takes place. They offer a wide variety of menu items, including sandwiches, burgers, pancakes, and steaks, suitable for any meal of the day. Since they are open 24 hours, you can visit at any time to enjoy your favorite food. During DEF CON, it can get crowded and the food preparation may slow down, so you might have to wait about 40 minutes to an hour after being seated. However, the prices are affordable and the portions are generous, making it a great choice for breakfast or lunch if you’re visiting LVCC.
Hot & Juicy
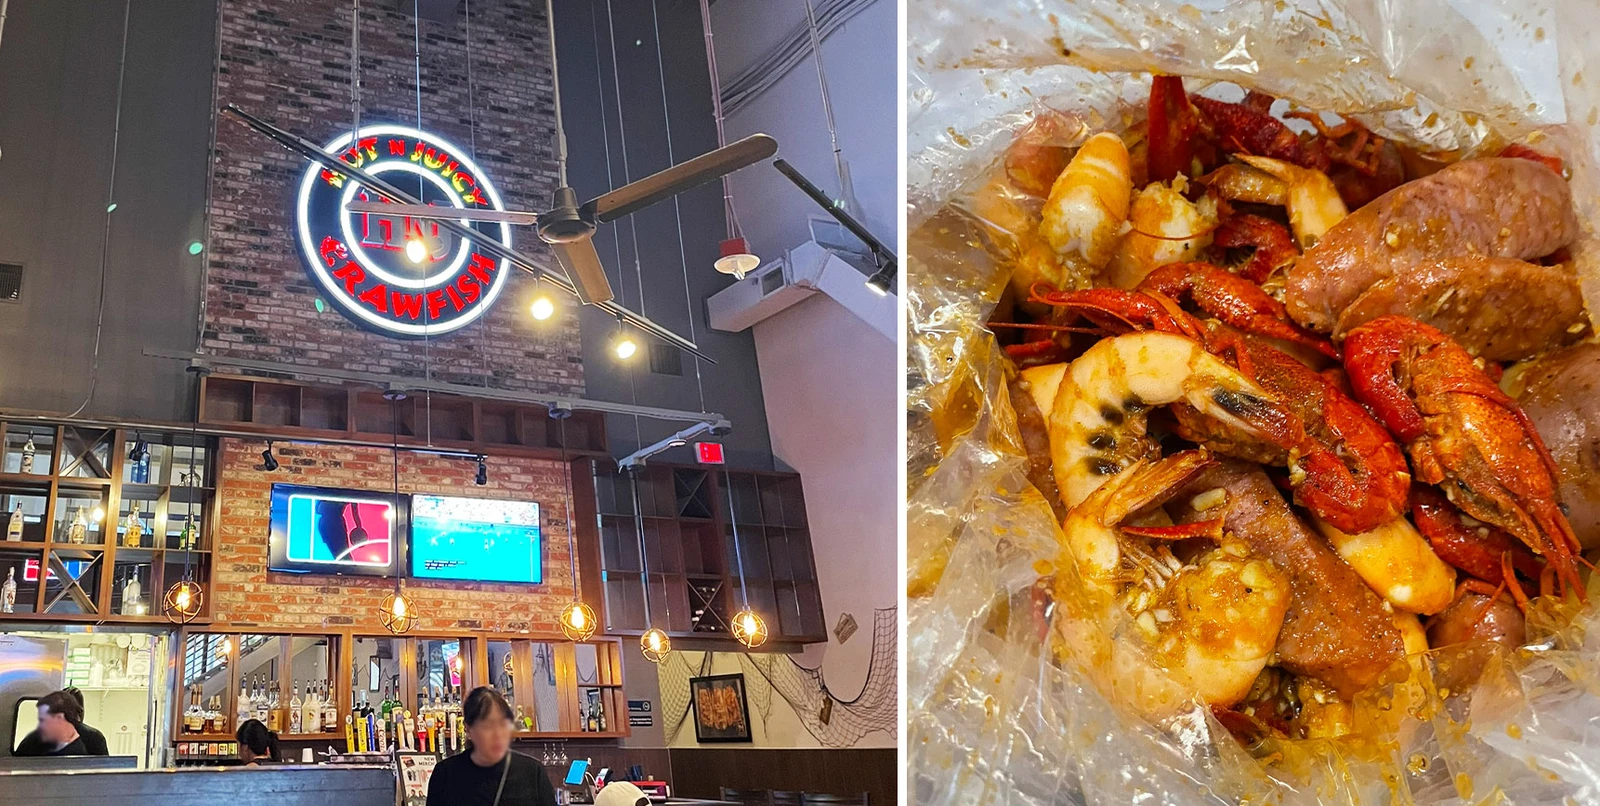
One of the popular restaurants among Koreans in Las Vegas is Hot & Juicy, a seafood boil specialty restaurant. Here, you can enjoy shrimp, crawfish, and king crab cooked with corn, potatoes, and sausage in a spicy sauce. Uniquely, the food is served not on a plate but directly in a bag, and you eat it using gloves. The food is incredibly delicious, and the spiciness captures the essence of American dining, making it a must-visit.
Overall, our first experience attending DEF CON was very meaningful.
We plan to continue researching various hacking techniques and strive to gain even more experience for the next event! 😊
Written by HanRyeol Park and Hyojin Lee