Contents
On August 1, 2025, the European Union (EU) officially enforced the RED (Radio Equipment Directive) 3.3 cybersecurity requirements for wireless and IoT devices.
This is not just a technical guideline—it is a legal obligation that every manufacturer of wireless products must comply with in order to enter the European market.
Why Is This Regulation So Critical?
Traditionally, RED focused mainly on electromagnetic compatibility and product safety.
Now, cybersecurity has become a mandatory requirement.
The following three clauses are now enforced from 2025:
3.3(d) : Protection of network resources and service availability
3.3(e) : Secure processing of personal and location data
3.3(f) : Prevention of fraud and counterfeiting in authentication and payment functions
This means that all wireless devices—from smart appliances and wearables to industrial IoT systems and
in-vehicle wireless modules—must undergo new cybersecurity validation before entering the EU market.
Impact on Businesses
As a non-deferrable regulation, failure to comply with RED 3.3 leads to serious risks:
🚫 Customs Rejection : Products blocked at EU ports and customs clearance
🚫 Sales Ban : Non-certified products prohibited from local distribution
🚫 Loss of Market Competitiveness : Delayed certification means losing the right market entry timing
For SMEs in particular, the lack of dedicated security experts and regulatory know-how can make compliance a major challenge.
👉 Even a short delay in certification could hold back your entire shipment.
How Should Companies Prepare?
Passing a lab test alone is not enough.
Compliance requires security-by-design from the early development stage, along with
technical documentation, security guidelines, and proof of compliance.
A step-by-step approach is essential:
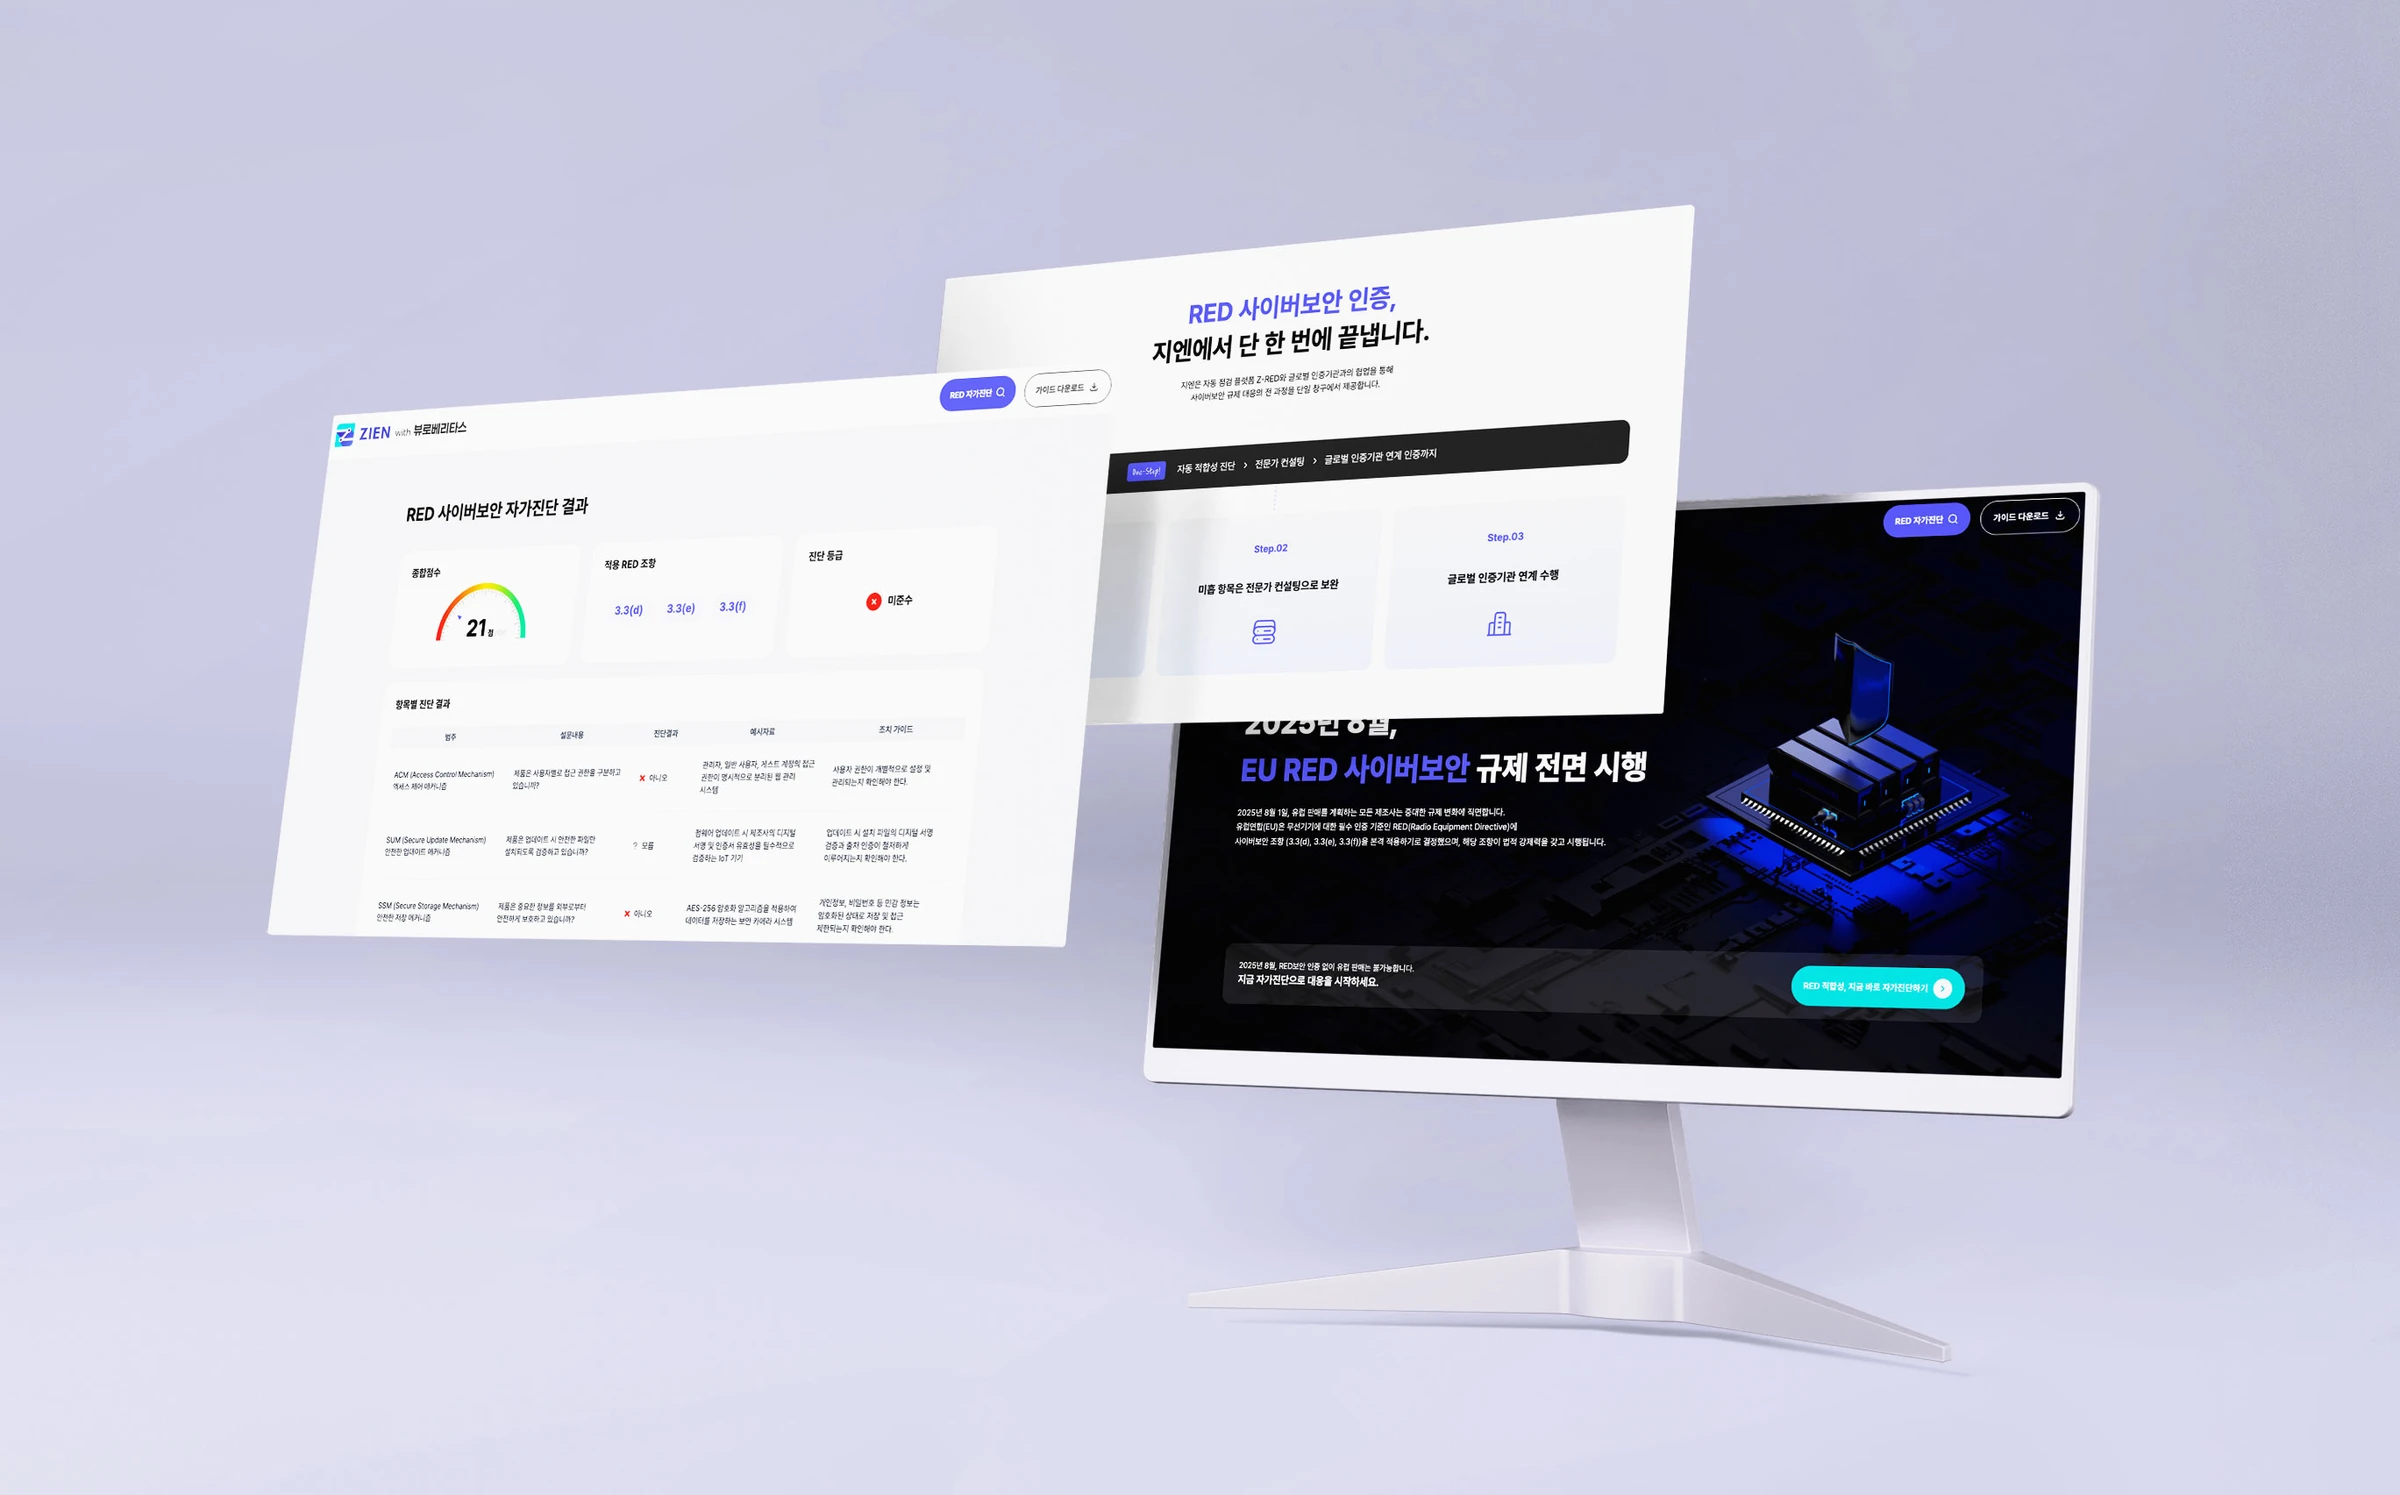
Self-assessment : Identify whether your product is subject to RED 3.3 and which areas are non-compliant
Security-by-design : Strengthen firmware, networking, and personal data protection
Technical documentation : Provide evidence for each regulatory clause
Accredited certification : Work with EU-approved certification bodies
ZIEN’s Solution: RED 3.3 Certification Consulting
ZIEN, in partnership with EU Notified Body Bureau Veritas, provides certification consulting for RED 3.3.
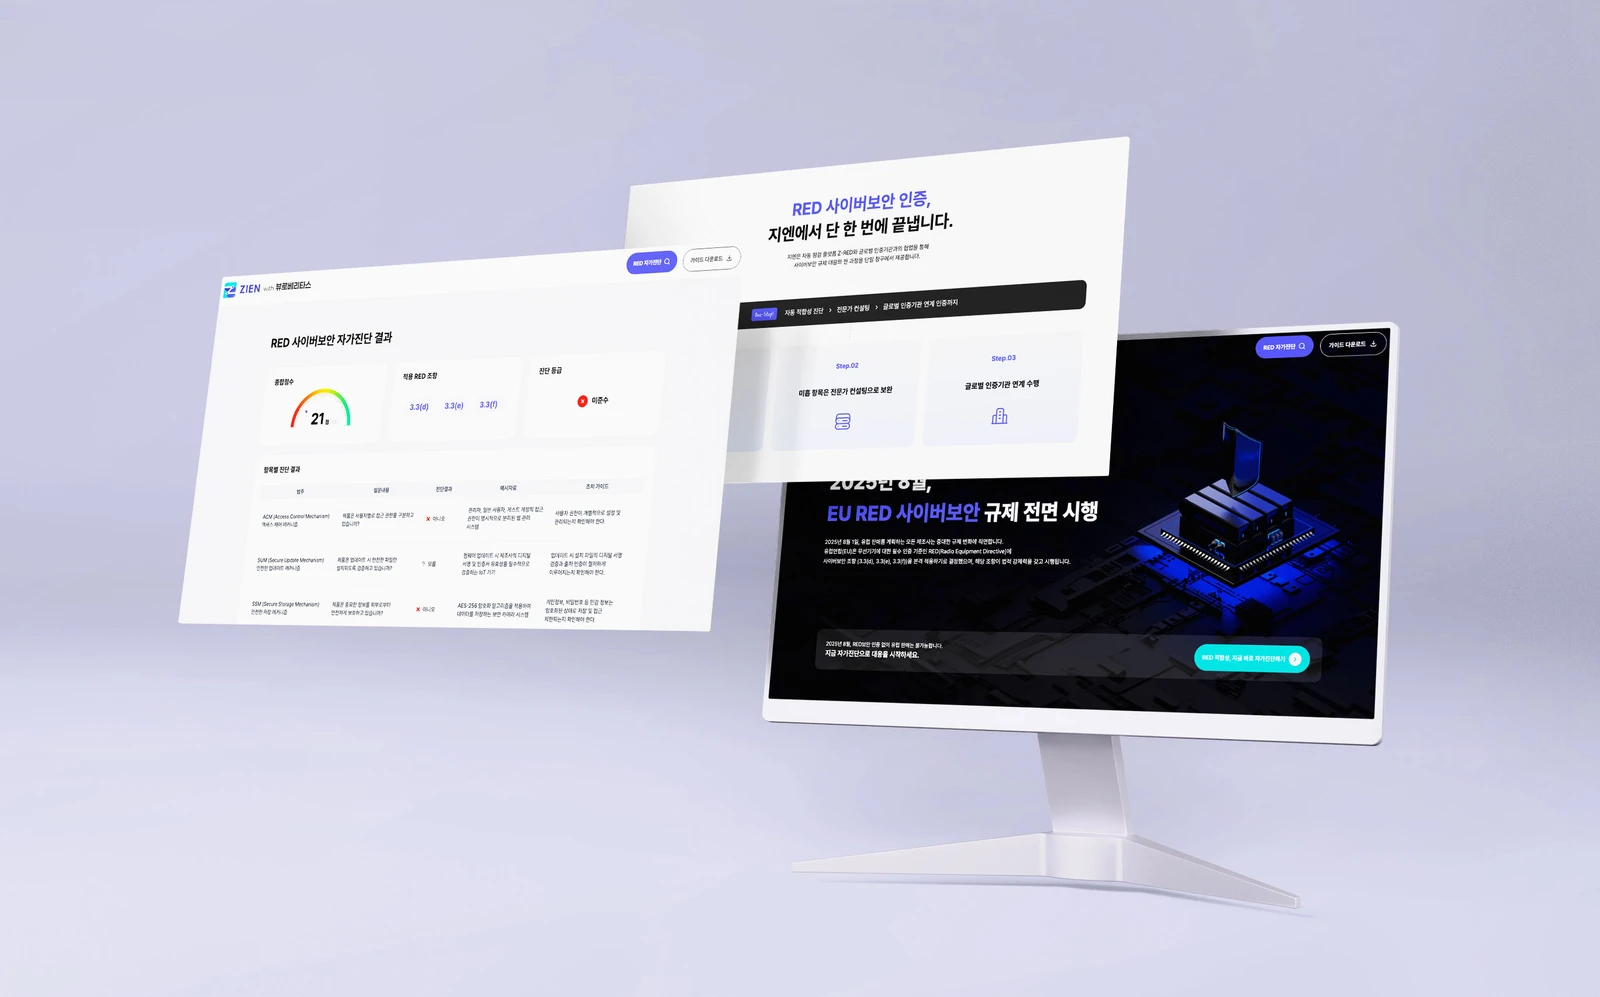
By consolidating the RED process into a single workflow, ZIEN significantly reduces both lead time and costs.
👉 Cut prep time in half—consult ZIEN now.
RED 3.3 is not optional
For any company exporting to Europe, RED 3.3 compliance is your license to operate.
With ZIEN’s expert consultants, businesses can meet these new cybersecurity requirements faster and with confidence.