RED Cybersecurity Requirements Are Now Mandatory for EU Market Access: Why You Must Act Now
Contents
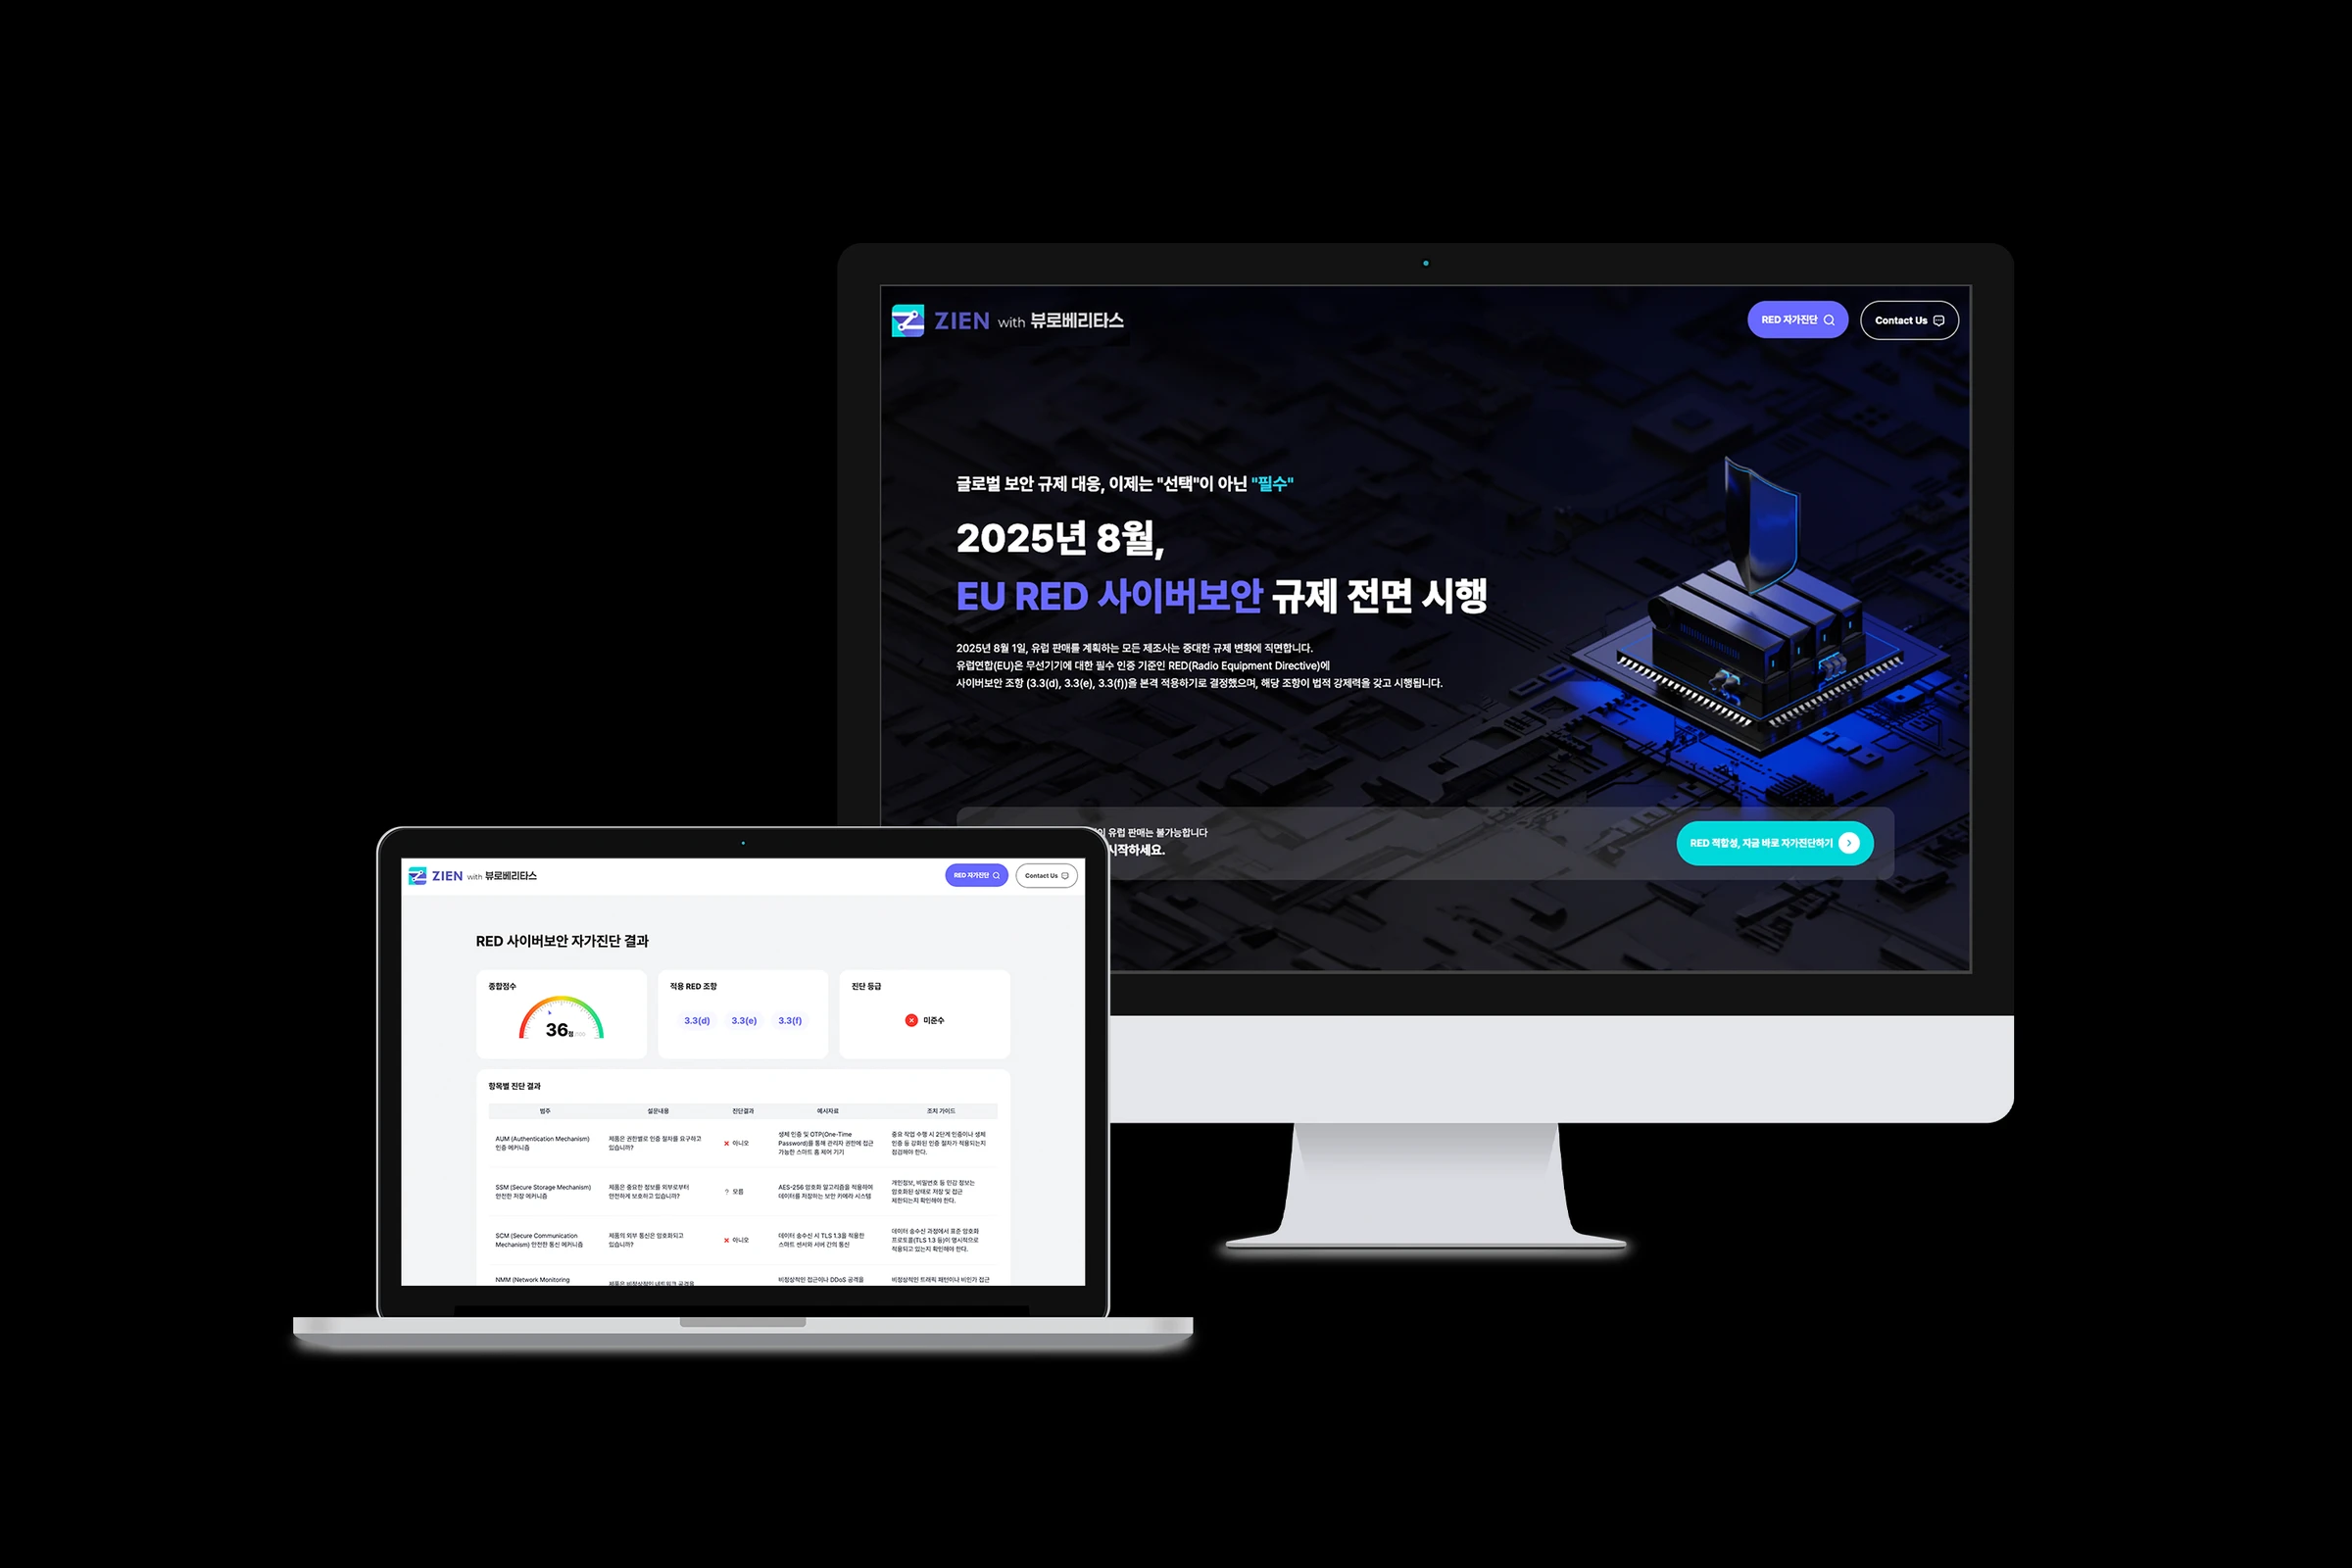
As of August 1, 2025, a significant regulatory change took effect for manufacturers of wireless-enabled devices entering the EU market. Products with Bluetooth, Wi-Fi, LTE, or other wireless functions are prohibited from being sold in Europe unless they fully comply with the RED Article 3.3 cybersecurity requirements.
Since RED certification is now mandatory for exporting to the EU, this regulation could have a major impact on a company's overall export strategy. If your organization's products fall within the scope of this regulation and you are not yet prepared, the time to act is now.
Overview of the EU RED Cybersecurity Requirements
The Radio Equipment Directive (RED) has been the mandatory certification framework for all wireless equipment sold in the EU since 2014. Among its provisions, Articles 3.3(d), 3.3(e), and 3.3(f)—which address cybersecurity—became fully mandatory on August 1, 2025, after a multi-year deferral.
All devices with wireless capabilities must now comply with these security requirements to maintain market access.
Key Cybersecurity Requirements
☑️ 3.3(d): Ensure protection of network resources and service continuity for wireless equipment.
☑️ 3.3(e): Safeguard the handling and processing of user personal and location data.
☑️ 3.3(f): Implement mechanisms to prevent fraud and counterfeiting of authentication and payment features.
Scope of Application
Internet-connected wireless devices: smartphones, tablets, laptops, IoT devices, smart home appliances, etc.
Payment and financial transaction devices: POS terminals, NFC payment terminals, etc.
Wearables and child safety devices: smartwatches, fitness bands, baby monitors, etc.
Industrial and automotive wireless equipment: industrial IoT modules, connected vehicles, drones, smart meters, etc.
Compliance is not just about testing. Manufacturers must submit a wide range of evidence, including technical documentation, security architecture designs, and implementation proof, to meet RED 3.3 standards.
The ZIEN and Bureau Veritas Advantage
Accredited Certification Body Partnership
Bureau Veritas is an official Notified Body designated to perform RED certifications, with a globally recognized reputation for credibility and expertise.
Cybersecurity Consulting
ZIEN brings deep security architecture expertise to support every step, from threat modeling to documentation and audit response.
One-Stop Certification Workflow
From diagnostics to audit support and coordination with certification bodies, ZIEN provides end-to-end support.
Who Needs to Prepare for RED 3.3?
We strongly recommend preparing for RED 3.3 now if your organization:
Is currently exporting to or planning to enter the EU market
Manufactures products with wireless functions (Bluetooth, Wi-Fi, LTE, etc.)
Needs to minimize the time and cost of certification preparation
Is an SME or mid-sized company that lacks in-house cybersecurity compliance expertise
For companies targeting the EU market, RED cybersecurity compliance is no longer optional.
Together with Bureau Veritas, ZIEN supports the entire RED certification process to help you reduce certification lead time, lower costs, and ensure full regulatory compliance.