Contents
The ZIEN research team participated in Pwn2Own Automotive 2025, held in Tokyo, Japan, from January 22 to 24, 2025. Pwn2Own is a prestigious event in the cybersecurity field where participants compete to discover and exploit vulnerabilities in various devices. This competition took place within the AUTOMOTIVE WORLD 2025 exhibition at Tokyo Big Sight.
Our team competed in the In-Vehicle Infotainment (IVI) Systems category. To prepare, we conducted a month-long, thorough analysis of the target device, identified vulnerabilities, and completed our competition registration.
We analyzed an IVI head unit manufactured by Kenwood and successfully exploited it using a Command Injection Attack to gain system privileges. Leveraging these privileges, further analysis revealed we could trigger Memory Corruption, enabling the execution of System Control Code to acquire administrative privileges. Based on these research findings, we participated in the competition.
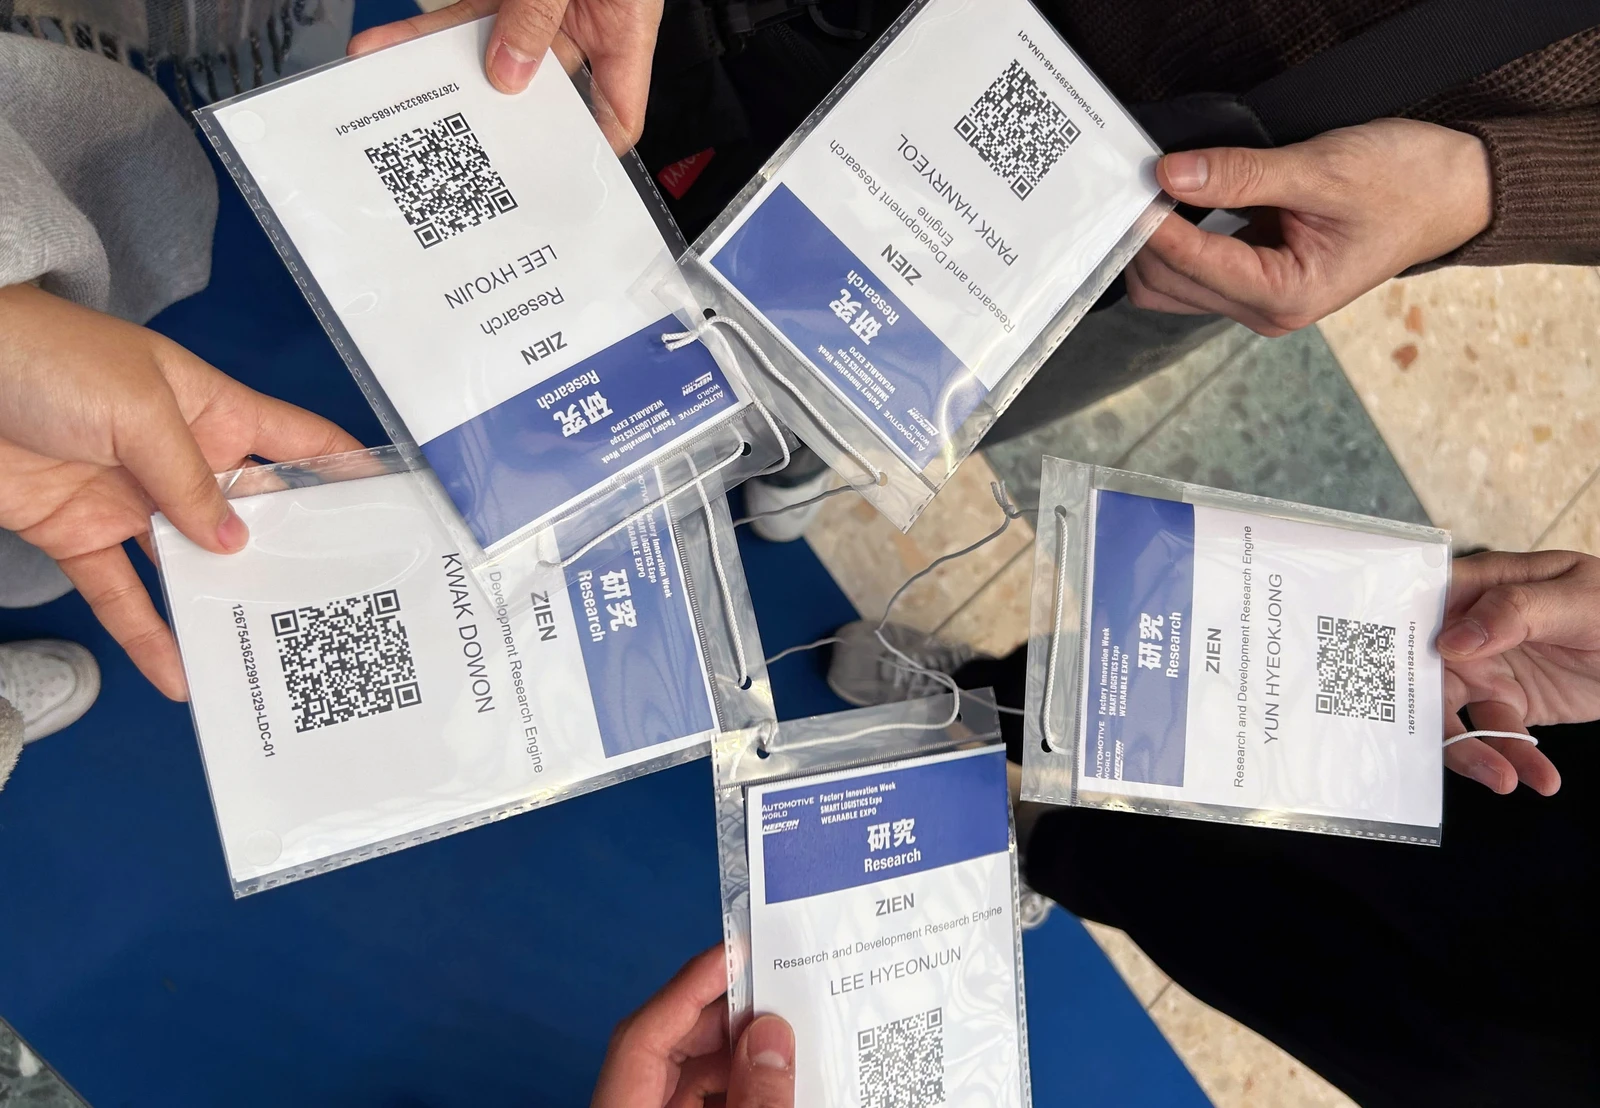
Prior to the event, we printed entry tickets for AUTOMOTIVE WORLD 2025, and placed them in the name badge holders distributed at the venue.
Pre-Competition Day: Draw and Schedule Confirmation
The schedule for Pwn2Own Automotive is finalized through a draw held the day before the competition.
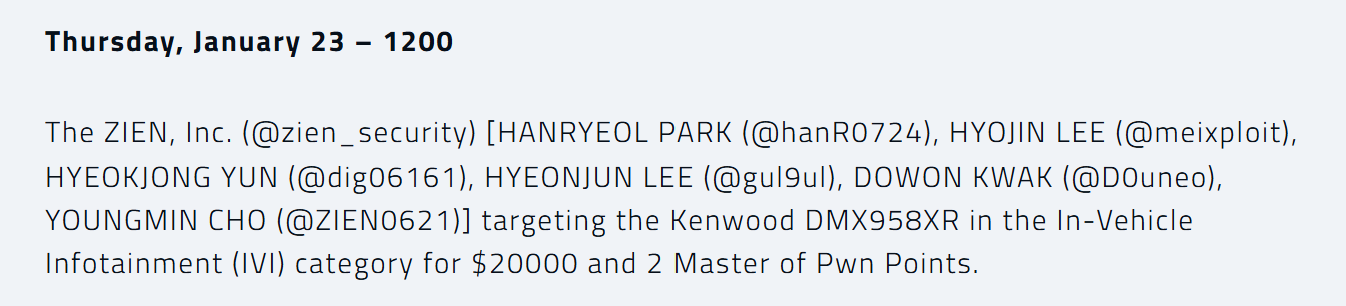
Arriving in Tokyo the day before, we watched the live draw and confirmed our presentation was scheduled for January 23 at 12:00. Upon reviewing the schedule, we discovered that three other teams were set to target the same device earlier in the competition.
On the first day of the competition (January 22), we monitored real-time updates on attack successes, hoping our prepared vulnerability wouldn’t overlap with theirs.
Competition Day: Challenge Amid Tension and Anticipation
The competition day finally arrived. The venue featured three stages, allowing three teams to compete simultaneously. Watching various teams attempt exploits in succession heightened the tension in the room. Earlier time slots included globally renowned security teams, notably Synacktiv, the winner of Pwn2Own Automotive 2025, whose cheers after a successful exploit amplified the electric atmosphere.
Pwn2Own Competition Format
Our turn arrived, and we competed on Stage A among the three stages.
Fifteen minutes before the competition, we were given time on stage to review basic setups and equipment. During this period, we verified the target device’s operation, checked network conditions, and finalized the exploit execution environment.
Pwn2Own consists of three 10-minute rounds. If an exploit succeeds within 10 minutes, the round ends; if not, the attempt continues in the second round. Success must be achieved within the three rounds, totaling 30 minutes.
Exploit Success: Earning Prizes and Master of Pwn Points
We successfully completed our exploit within the allotted 30 minutes. The thrill of success was indescribable, feeling like a rewarding culmination of our efforts.
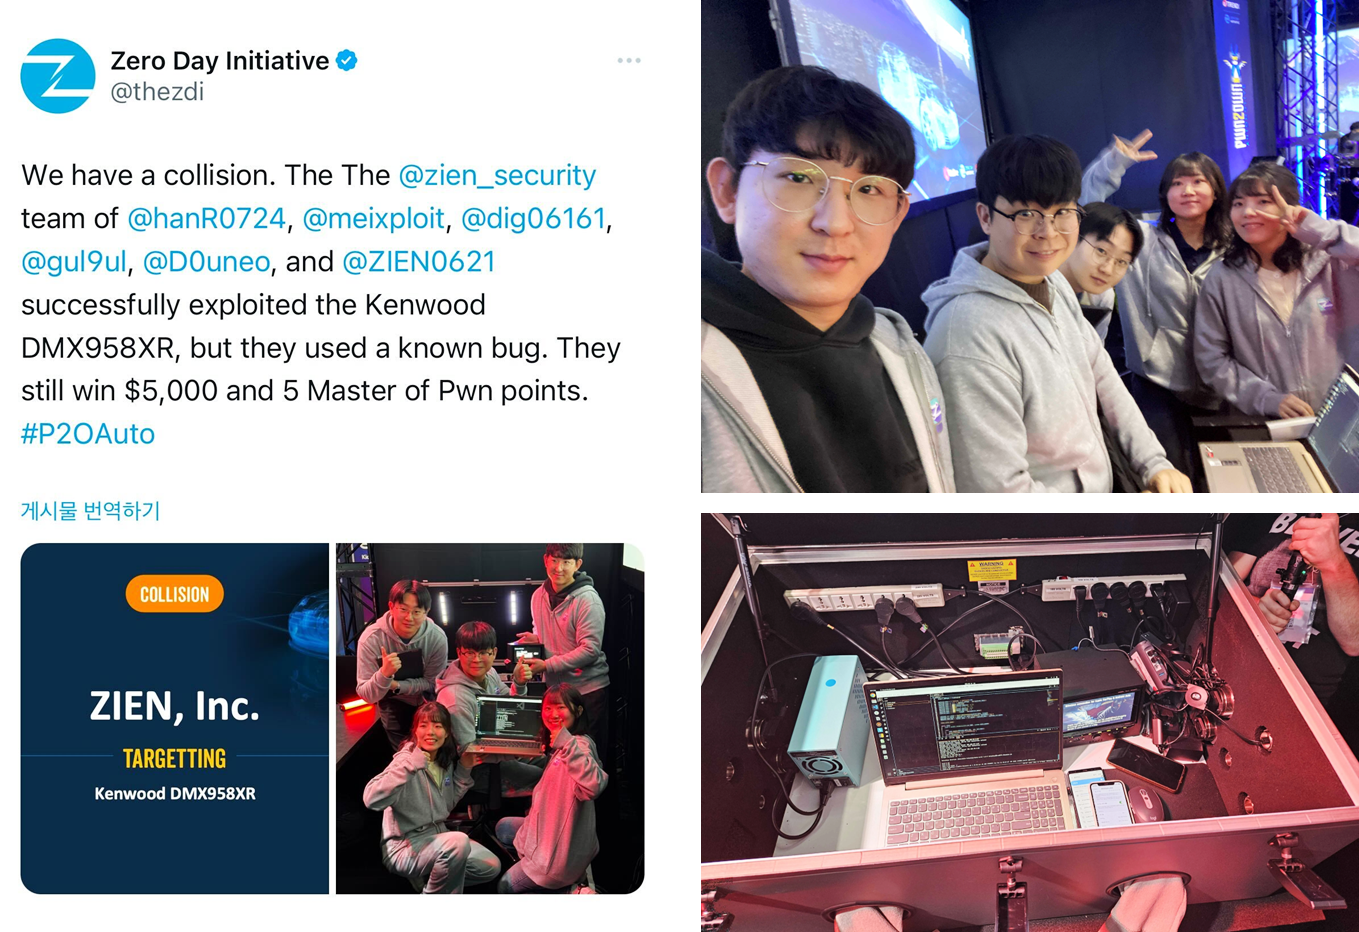
After the exploit, we were escorted by competition staff to the Backroom, where representatives from ZDI, VicOne, and the device manufacturer verified our exploit. We submitted a white paper detailing our successful exploit, and the reviewers evaluated whether it overlapped with previously reported vulnerabilities. They highly praised the completeness of our white paper, noting, “This is the most well-organized white paper we’ve seen,” and offered additional praise. We answered follow-up questions about the exploit’s execution and the vulnerability’s severity, providing detailed technical explanations based on our analysis.
However, we learned that the same vulnerability had been discovered the previous day. As a result, due to the duplicate finding, we concluded our Pwn2Own Automotive 2025 challenge with a $5,000 prize and 5 Master of Pwn points.
Our Next Challenge as an XIoT Security Convergence Company
Participating in this competition allowed us to experience the latest automotive security trends firsthand and network with global security experts. It also served as an opportunity to further enhance our capabilities as security researchers through real-world exploit execution.
This experience validated our technical expertise in the automotive security market and affirmed our global research capabilities. The vulnerabilities and insights gained are expected to significantly contribute to the development of ZIEN’s solution, ‘Z-IoT.’
However, we won’t stop here. For the next Pwn2Own, we will prepare more thoroughly to achieve flawless results, aiming for a SUCCESS rather than a COLLISION. We will continuously research and innovate, challenging a wider range of IoT devices.
Moving forward, ZIEN remains committed to ongoing research and innovation to strengthen security for automotive and various IoT devices. This competition experience will serve as a foundation for achieving our mission of building smart, secure IoT environments, allowing us to deliver even safer solutions to our customers. ☺️